Questionnaire Autopilot 1.7.4

Your security program, on your own computer.

Readiness for SOC 2, ISO 27001, NIST CSF, HIPAA, PCI DSS and NIS2 from one assessment. Policies written for you. Risks, vendors and incidents with every deadline tracked. Security questionnaires answered only from what you approved.

Windows, macOS and Linux. No account, no subscription, nothing uploaded.

SOC 238 criteria
ISO 2700193 controls
NIST CSF 2.022 categories
CIS Controls18 controls
HIPAA19 standards
PCI DSS 4.012 requirements
NIS2Art. 21 and 23
Cyber insurance12 controls

Everything a security lead tracks, on one screen.

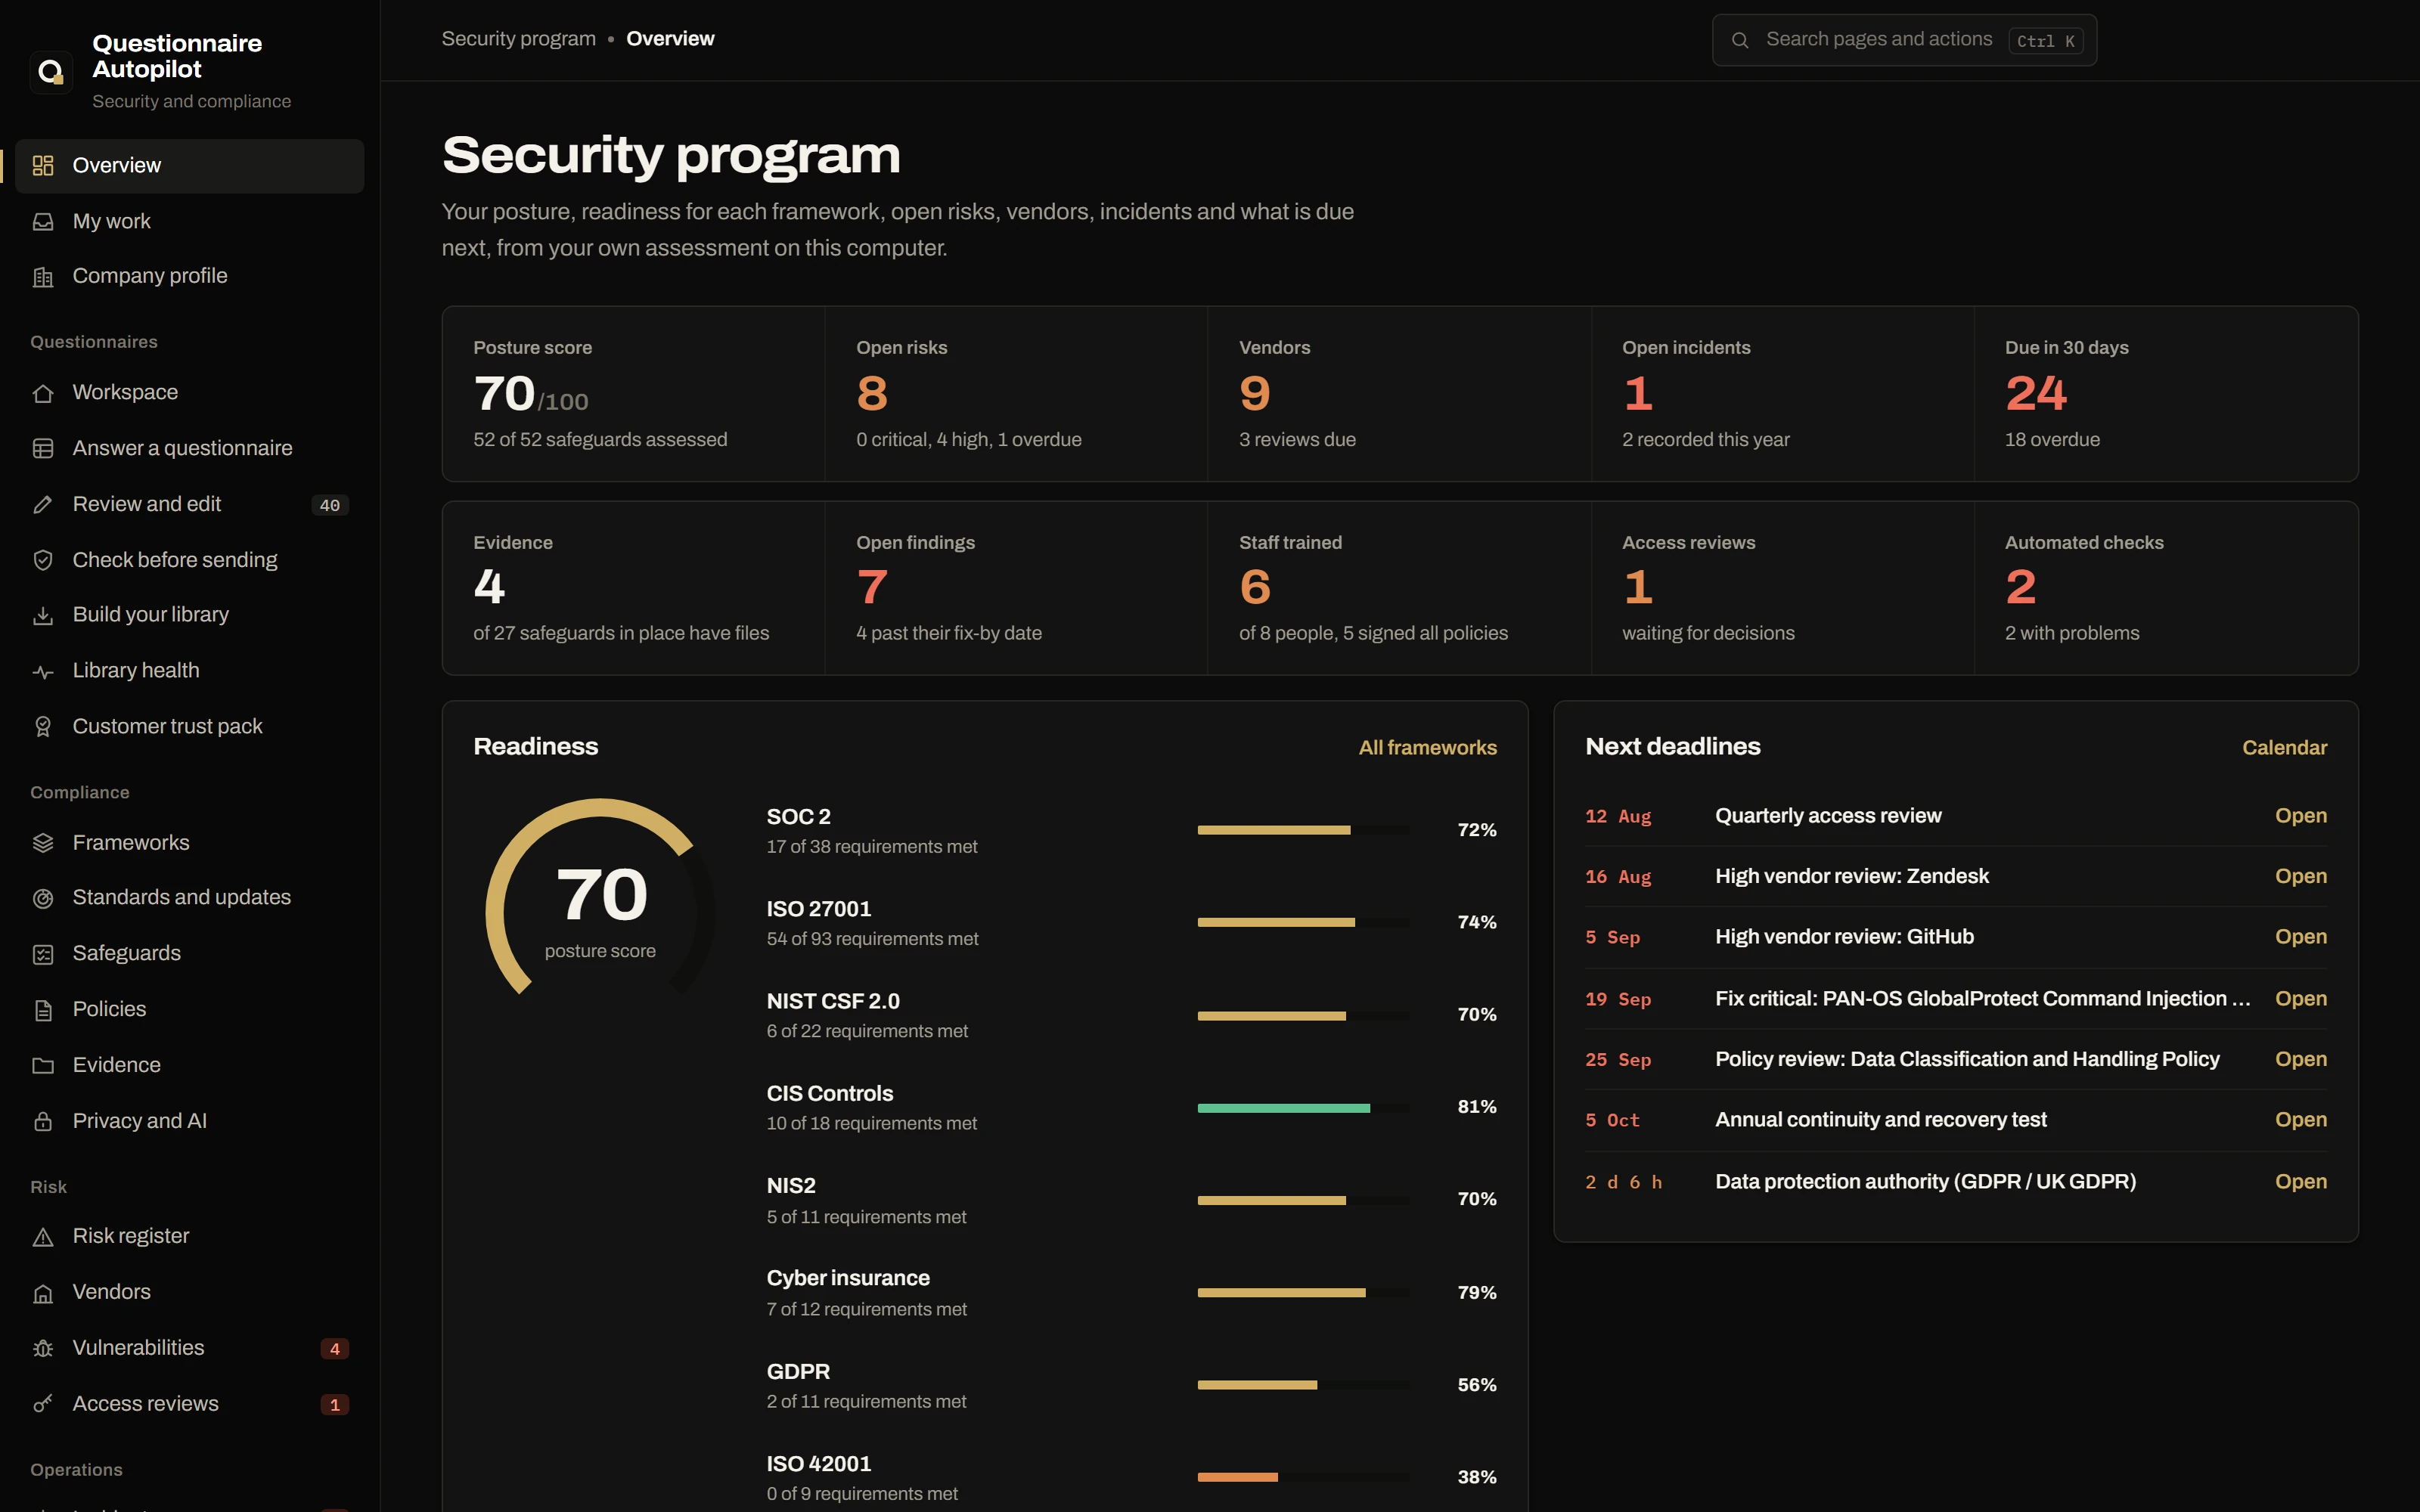
Real captures of the app, using Examplify Inc., the fictional company included as sample data.

The security program overview: posture score, evidence, findings, training and checks, readiness for each framework and next deadlines
296requirements in 16 frameworks, mapped to 52 safeguards you assess once
17security policies written from your profile, signed off by your staff
10notification clocks per incident: insurer, regulators, customers
$99once, for your organization, on up to three computers

Built for the work, not for a demo.

Each module produces something you can hand to an auditor, a board, an insurer or a customer. Every file stays on your computer, in formats you own: Word, Excel and HTML.

01 Compliance readiness

Assess once. See every framework.

Answer 52 safeguard questions: in place, partly, planned, not in place or not applicable. Readiness for every framework you track is calculated requirement by requirement, with the gaps that matter most listed first.

  • SOC 2, ISO 27001:2022 Annex A, NIST CSF 2.0, CIS v8.1, HIPAA, PCI DSS 4.0, NIS2, GDPR, CMMC Level 1, NIST 800-171, Cyber Essentials, Essential Eight and cyber insurance
  • AI governance: ISO/IEC 42001, the EU AI Act and NIST AI RMF
  • An ISO 27001 Statement of Applicability, ready for your auditor
  • Your approved questionnaire answers count as evidence
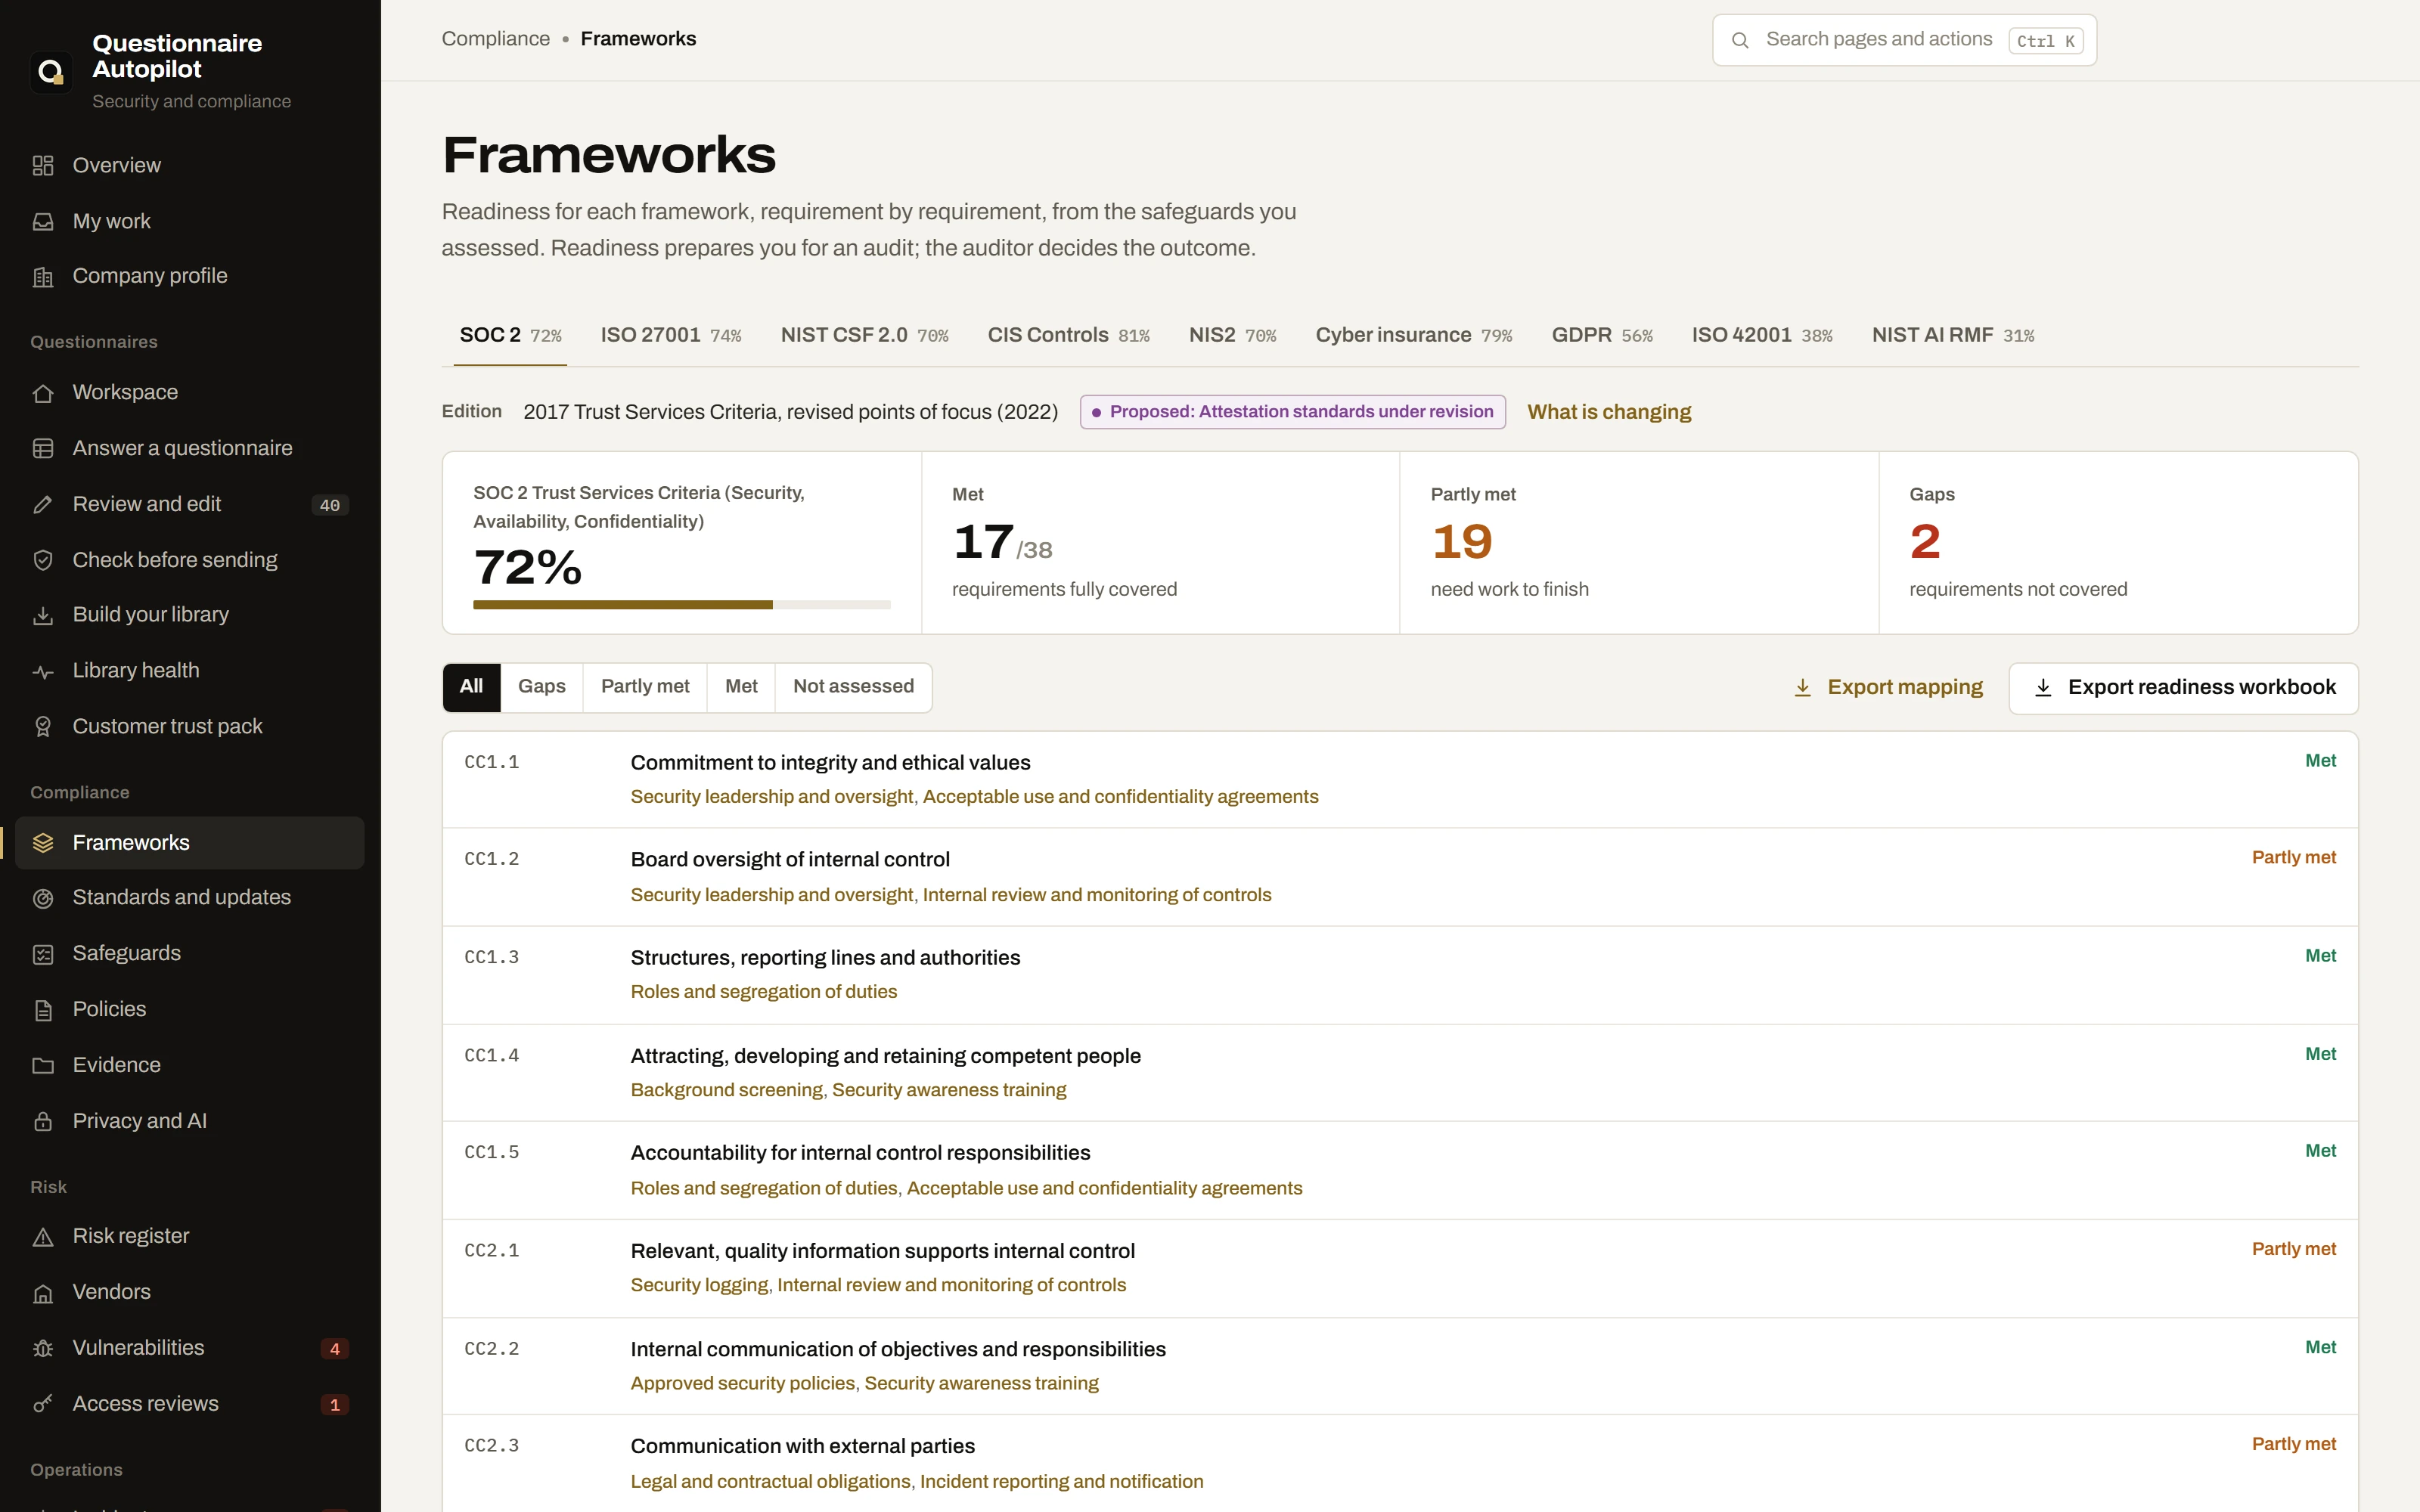
How readiness works
SOC 2 readiness at 72 percent, with each criterion, the safeguards that cover it and its state
02 Incident response

Every deadline, counting down.

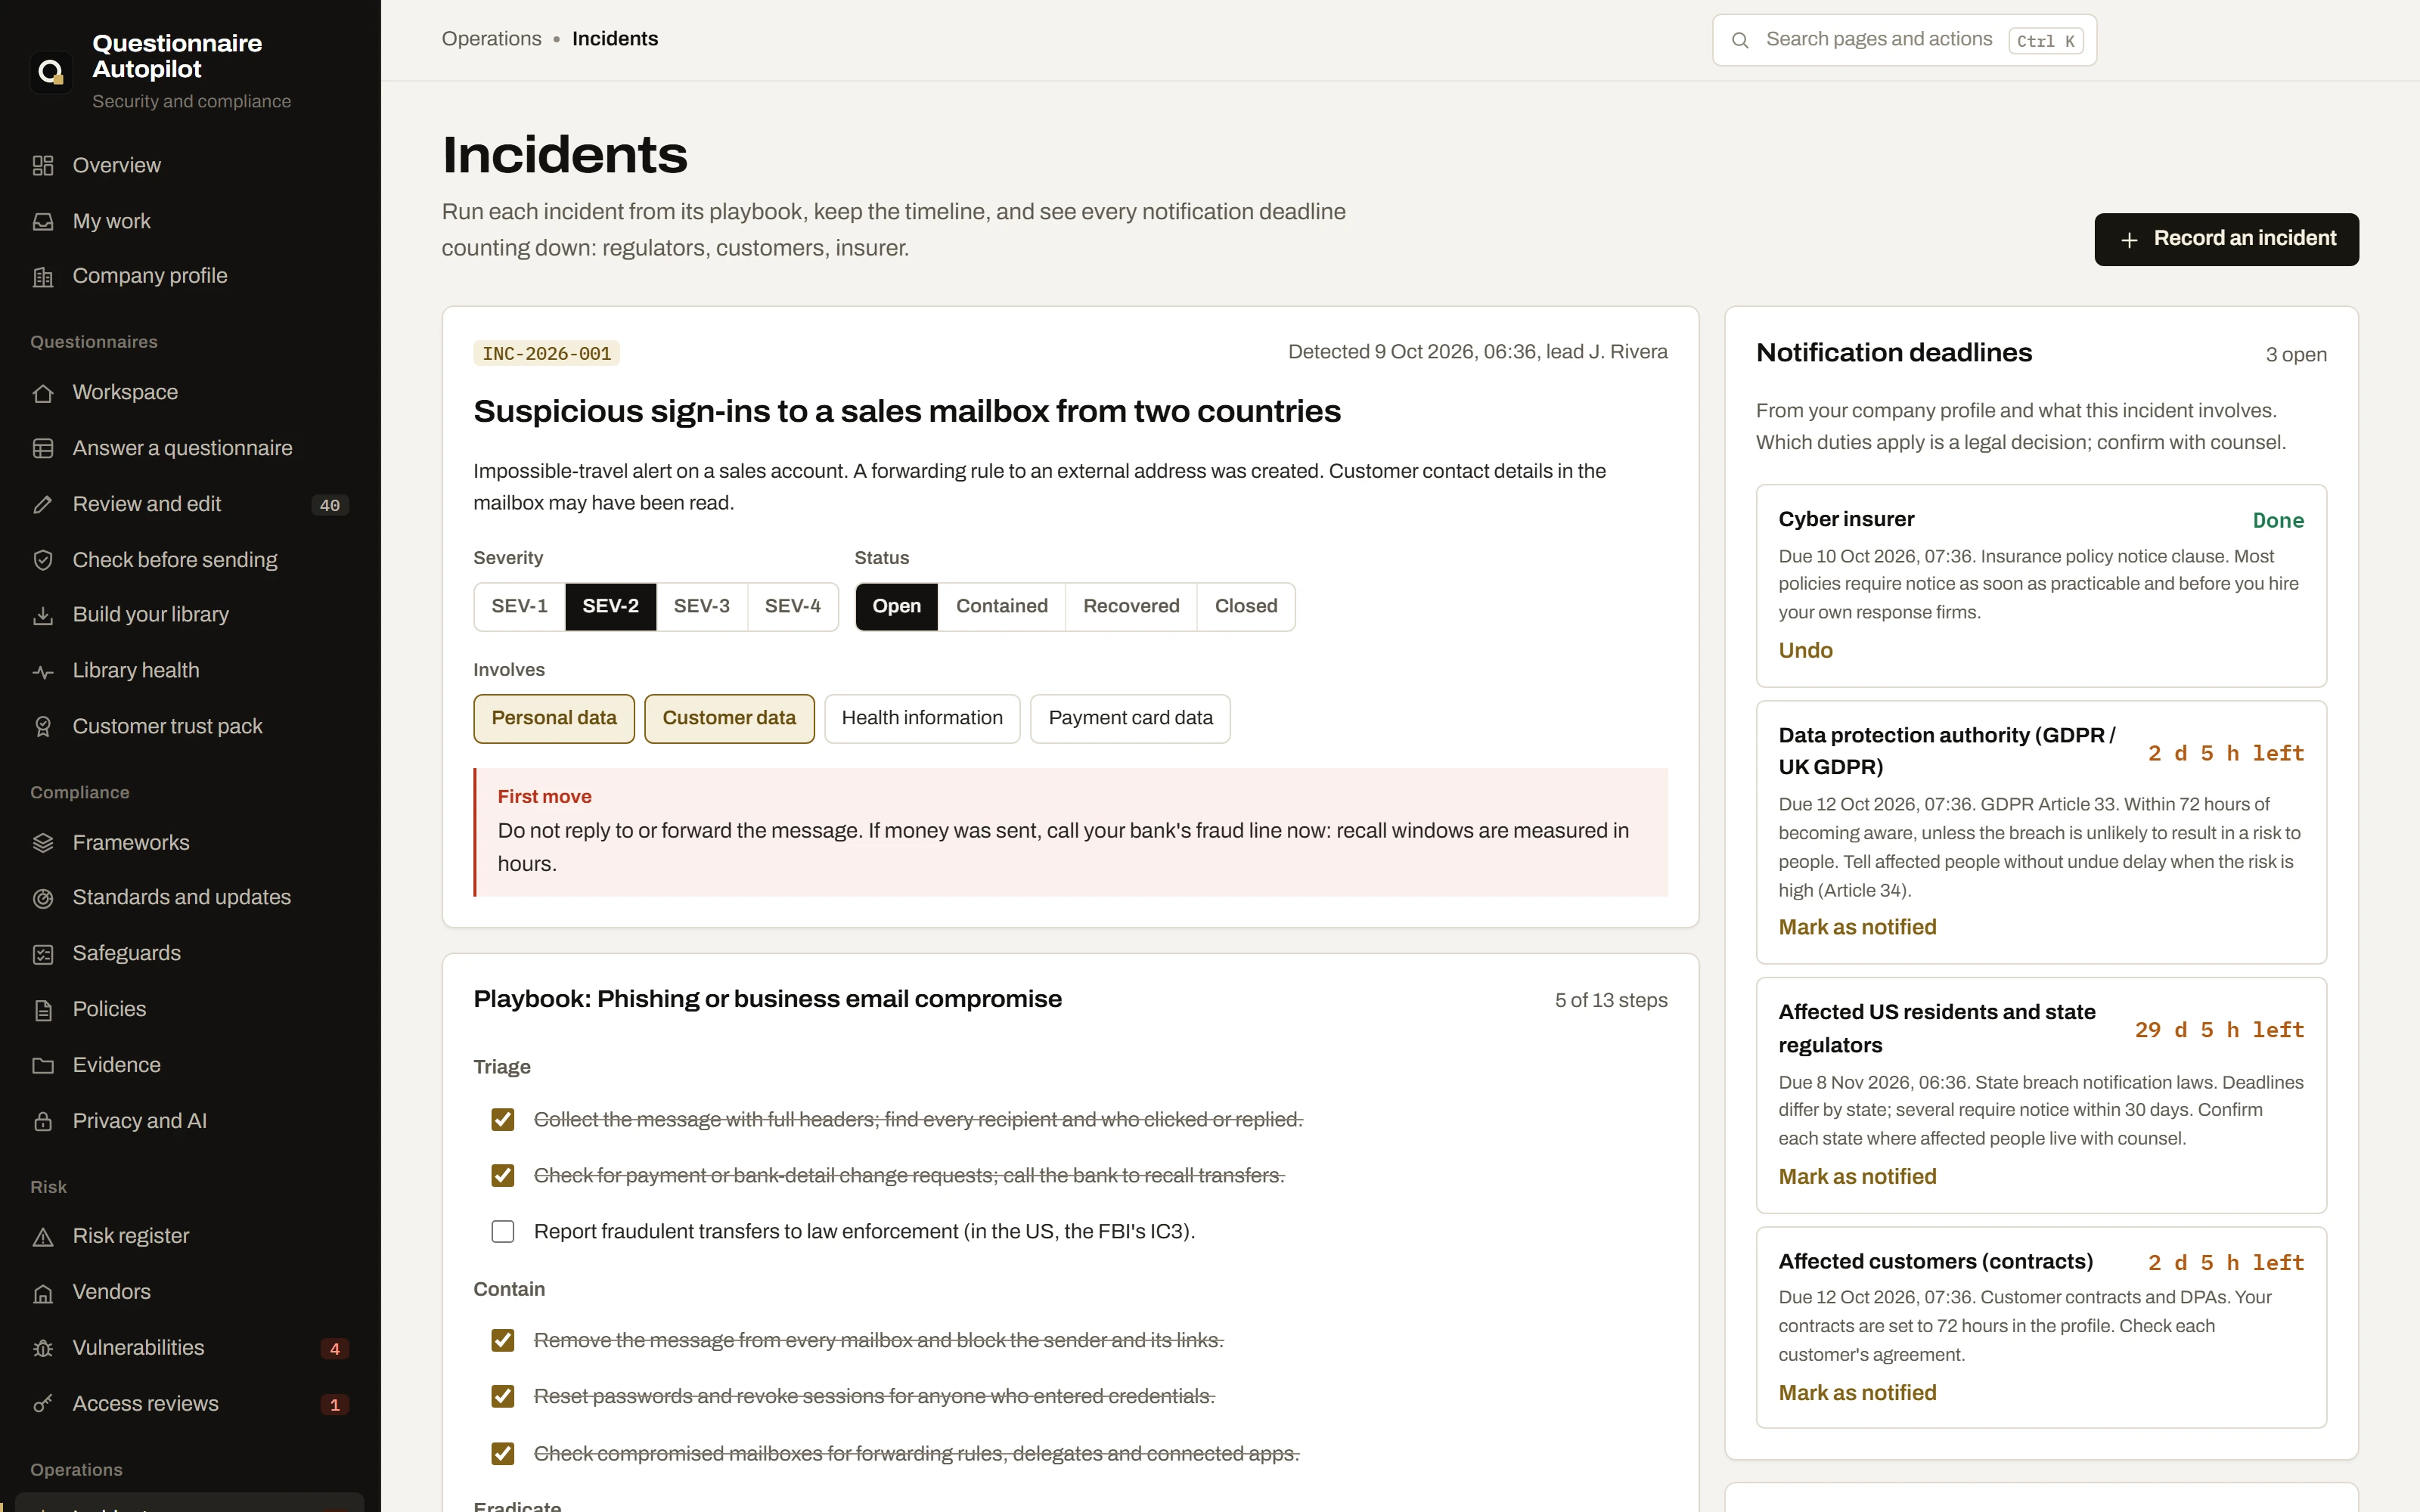
Record an incident and the app lists who must be told and by when: your cyber insurer, the data protection authority under GDPR, NIS2 and DORA authorities, the SEC, HHS, NY DFS, card brands, US states and your customers. Run the response from a playbook for the kind of incident you have.

  • Playbooks for ransomware, business email compromise, account takeover, data exposure and five more
  • A timeline, lessons learned and an incident report for leadership, insurer and counsel
Incident response in the guide
An open incident with its playbook steps and notification deadlines counting down
03 Third-party risk

Know which vendors can hurt you.

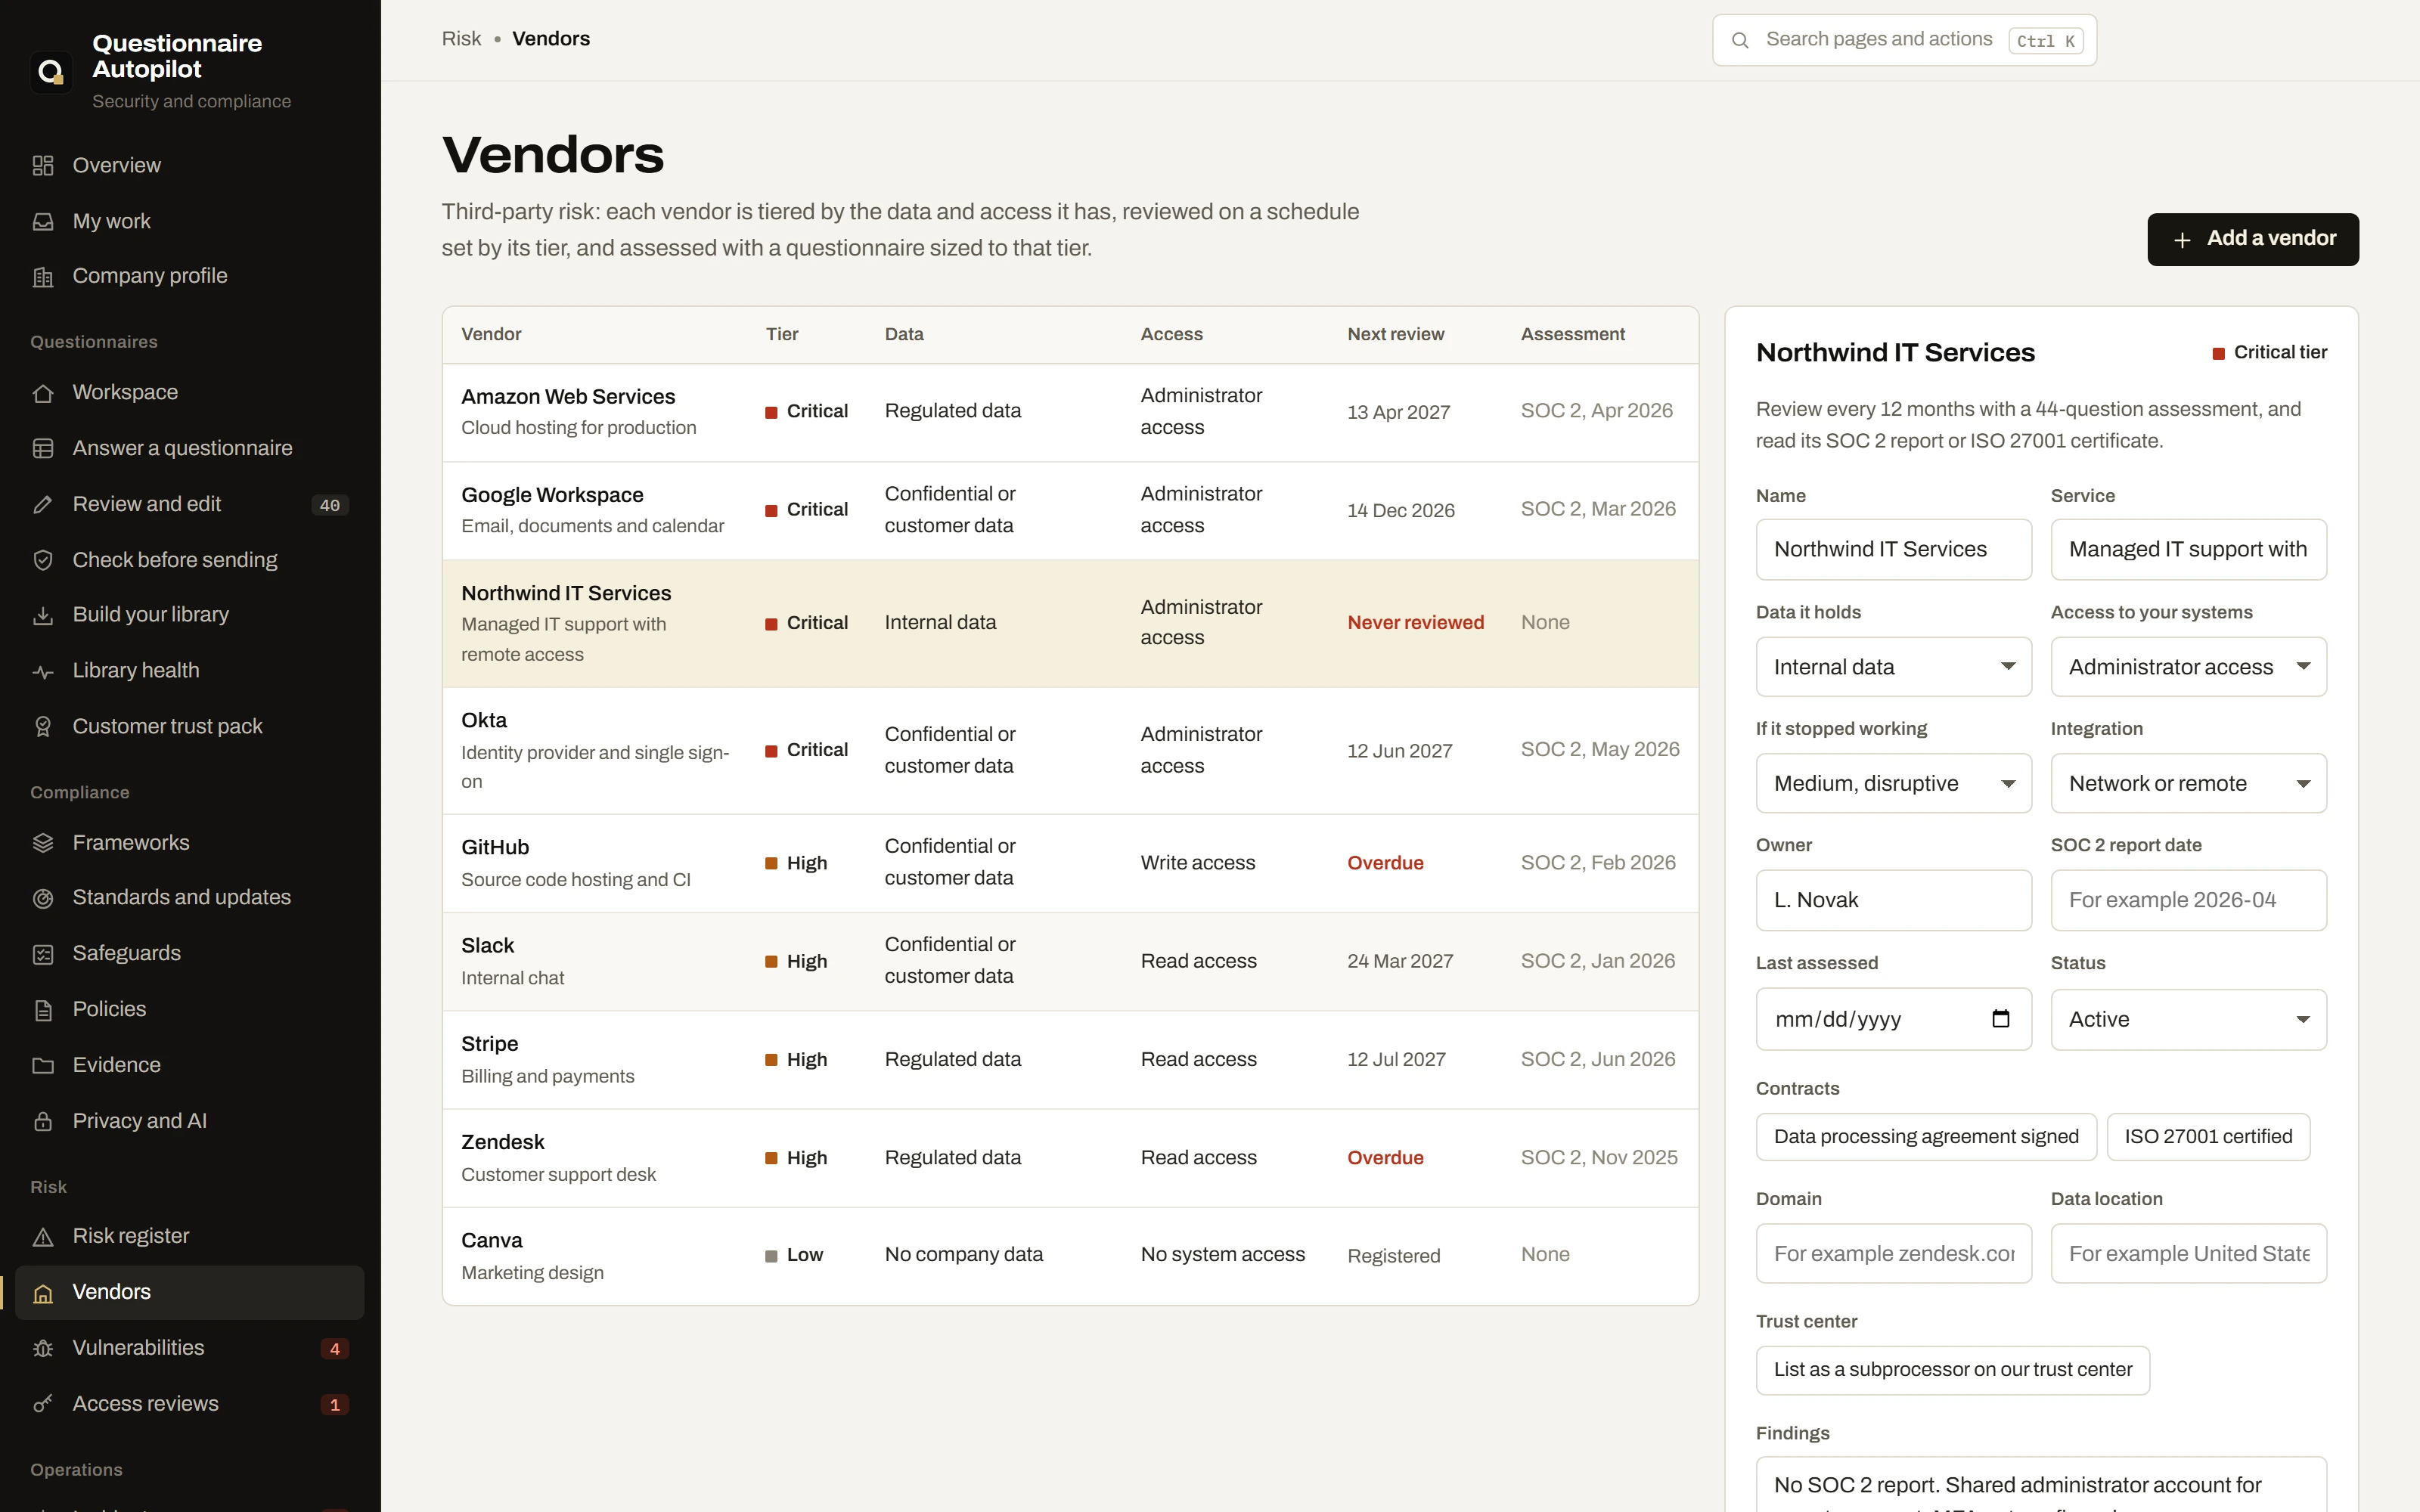
Each vendor is tiered Critical, High, Moderate or Low from the data it holds, the access it has, how much you depend on it and how it connects. The tier sets the review schedule and the size of the questionnaire you send. Score the answers when they come back.

  • Vendor security questionnaires in Excel, sized to the tier
  • Scored answers with red flags and residual risk
  • Reviews on your compliance calendar
Vendor risk in the guide
The vendor register with tiers, data, access and next review dates
04 Risk register and policies

Risks with owners. Policies with signatures.

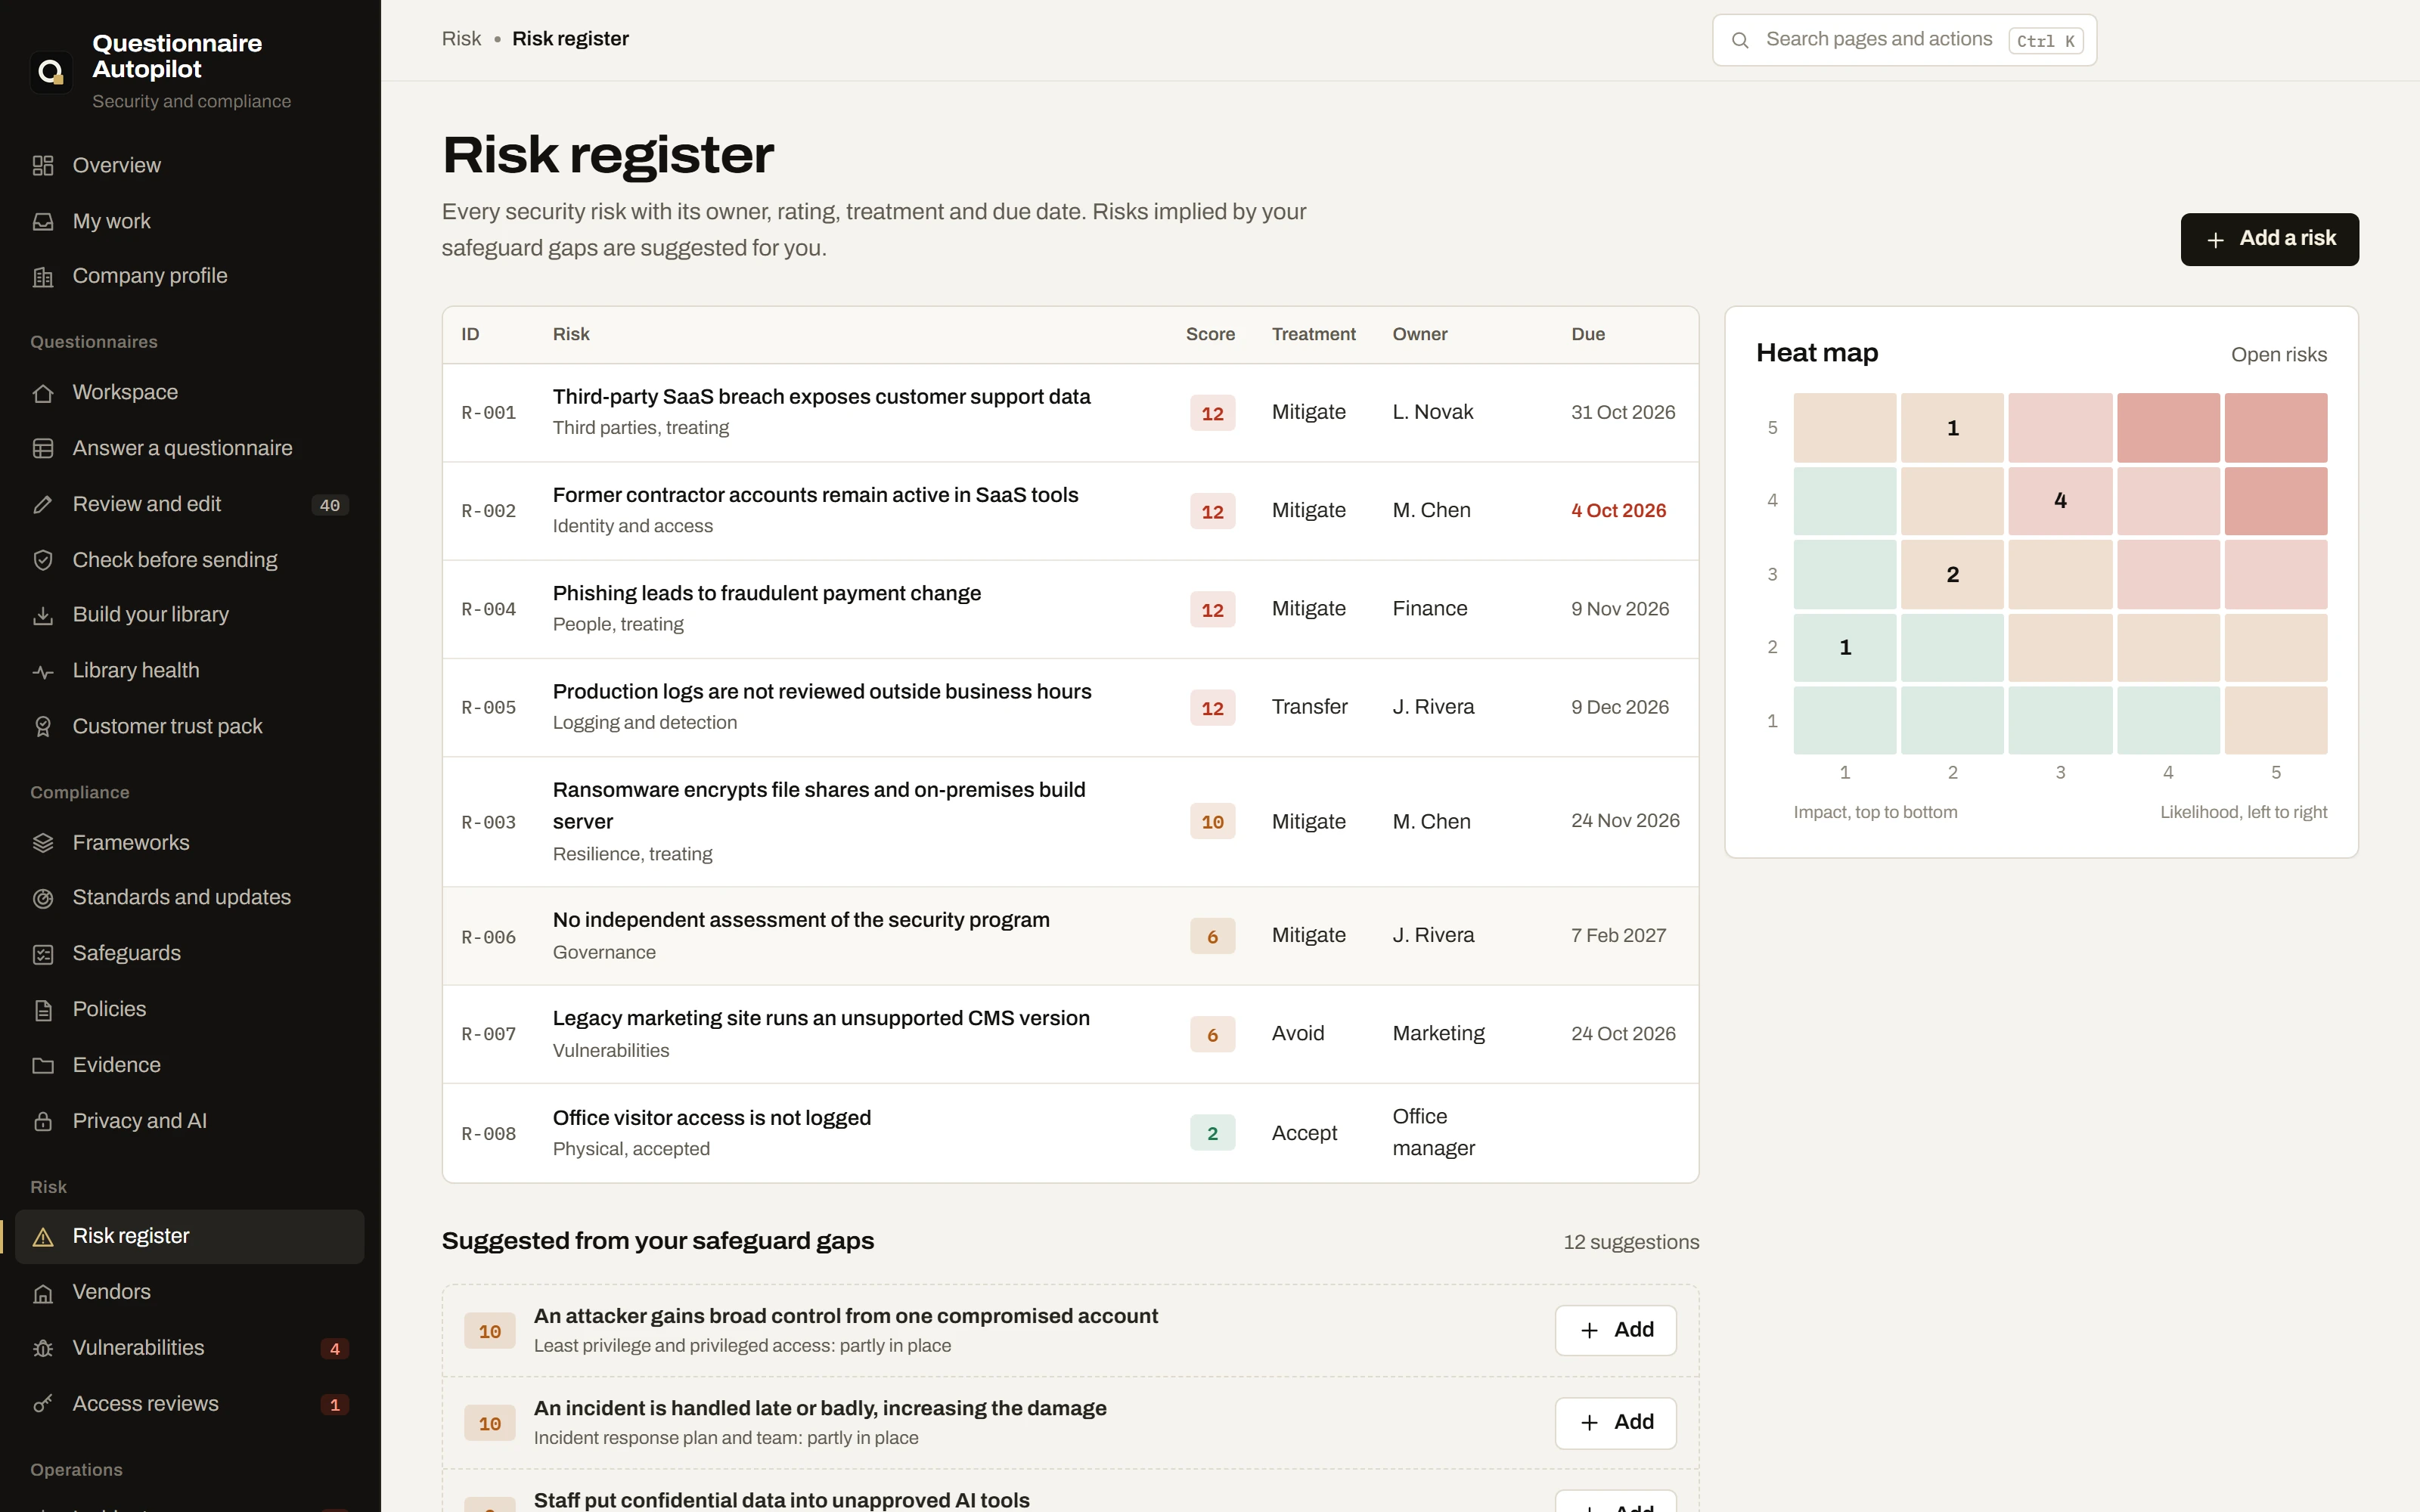
Keep every risk with its likelihood, impact, treatment, owner and due date, on a heat map leadership can read. Risks are suggested from your safeguard gaps. Seventeen security policies are written from your company profile, with framework references, ready to adapt and approve.

  • Policies as Word, HTML and Markdown, with approval and yearly review dates
  • Which staff signed which version, and who completed security training
  • A posture report for leadership or the board, printable to PDF
Risks and policies in the guide
The risk register with scores, treatments, owners and the heat map
05 Security questionnaires

Answers you can stand behind.

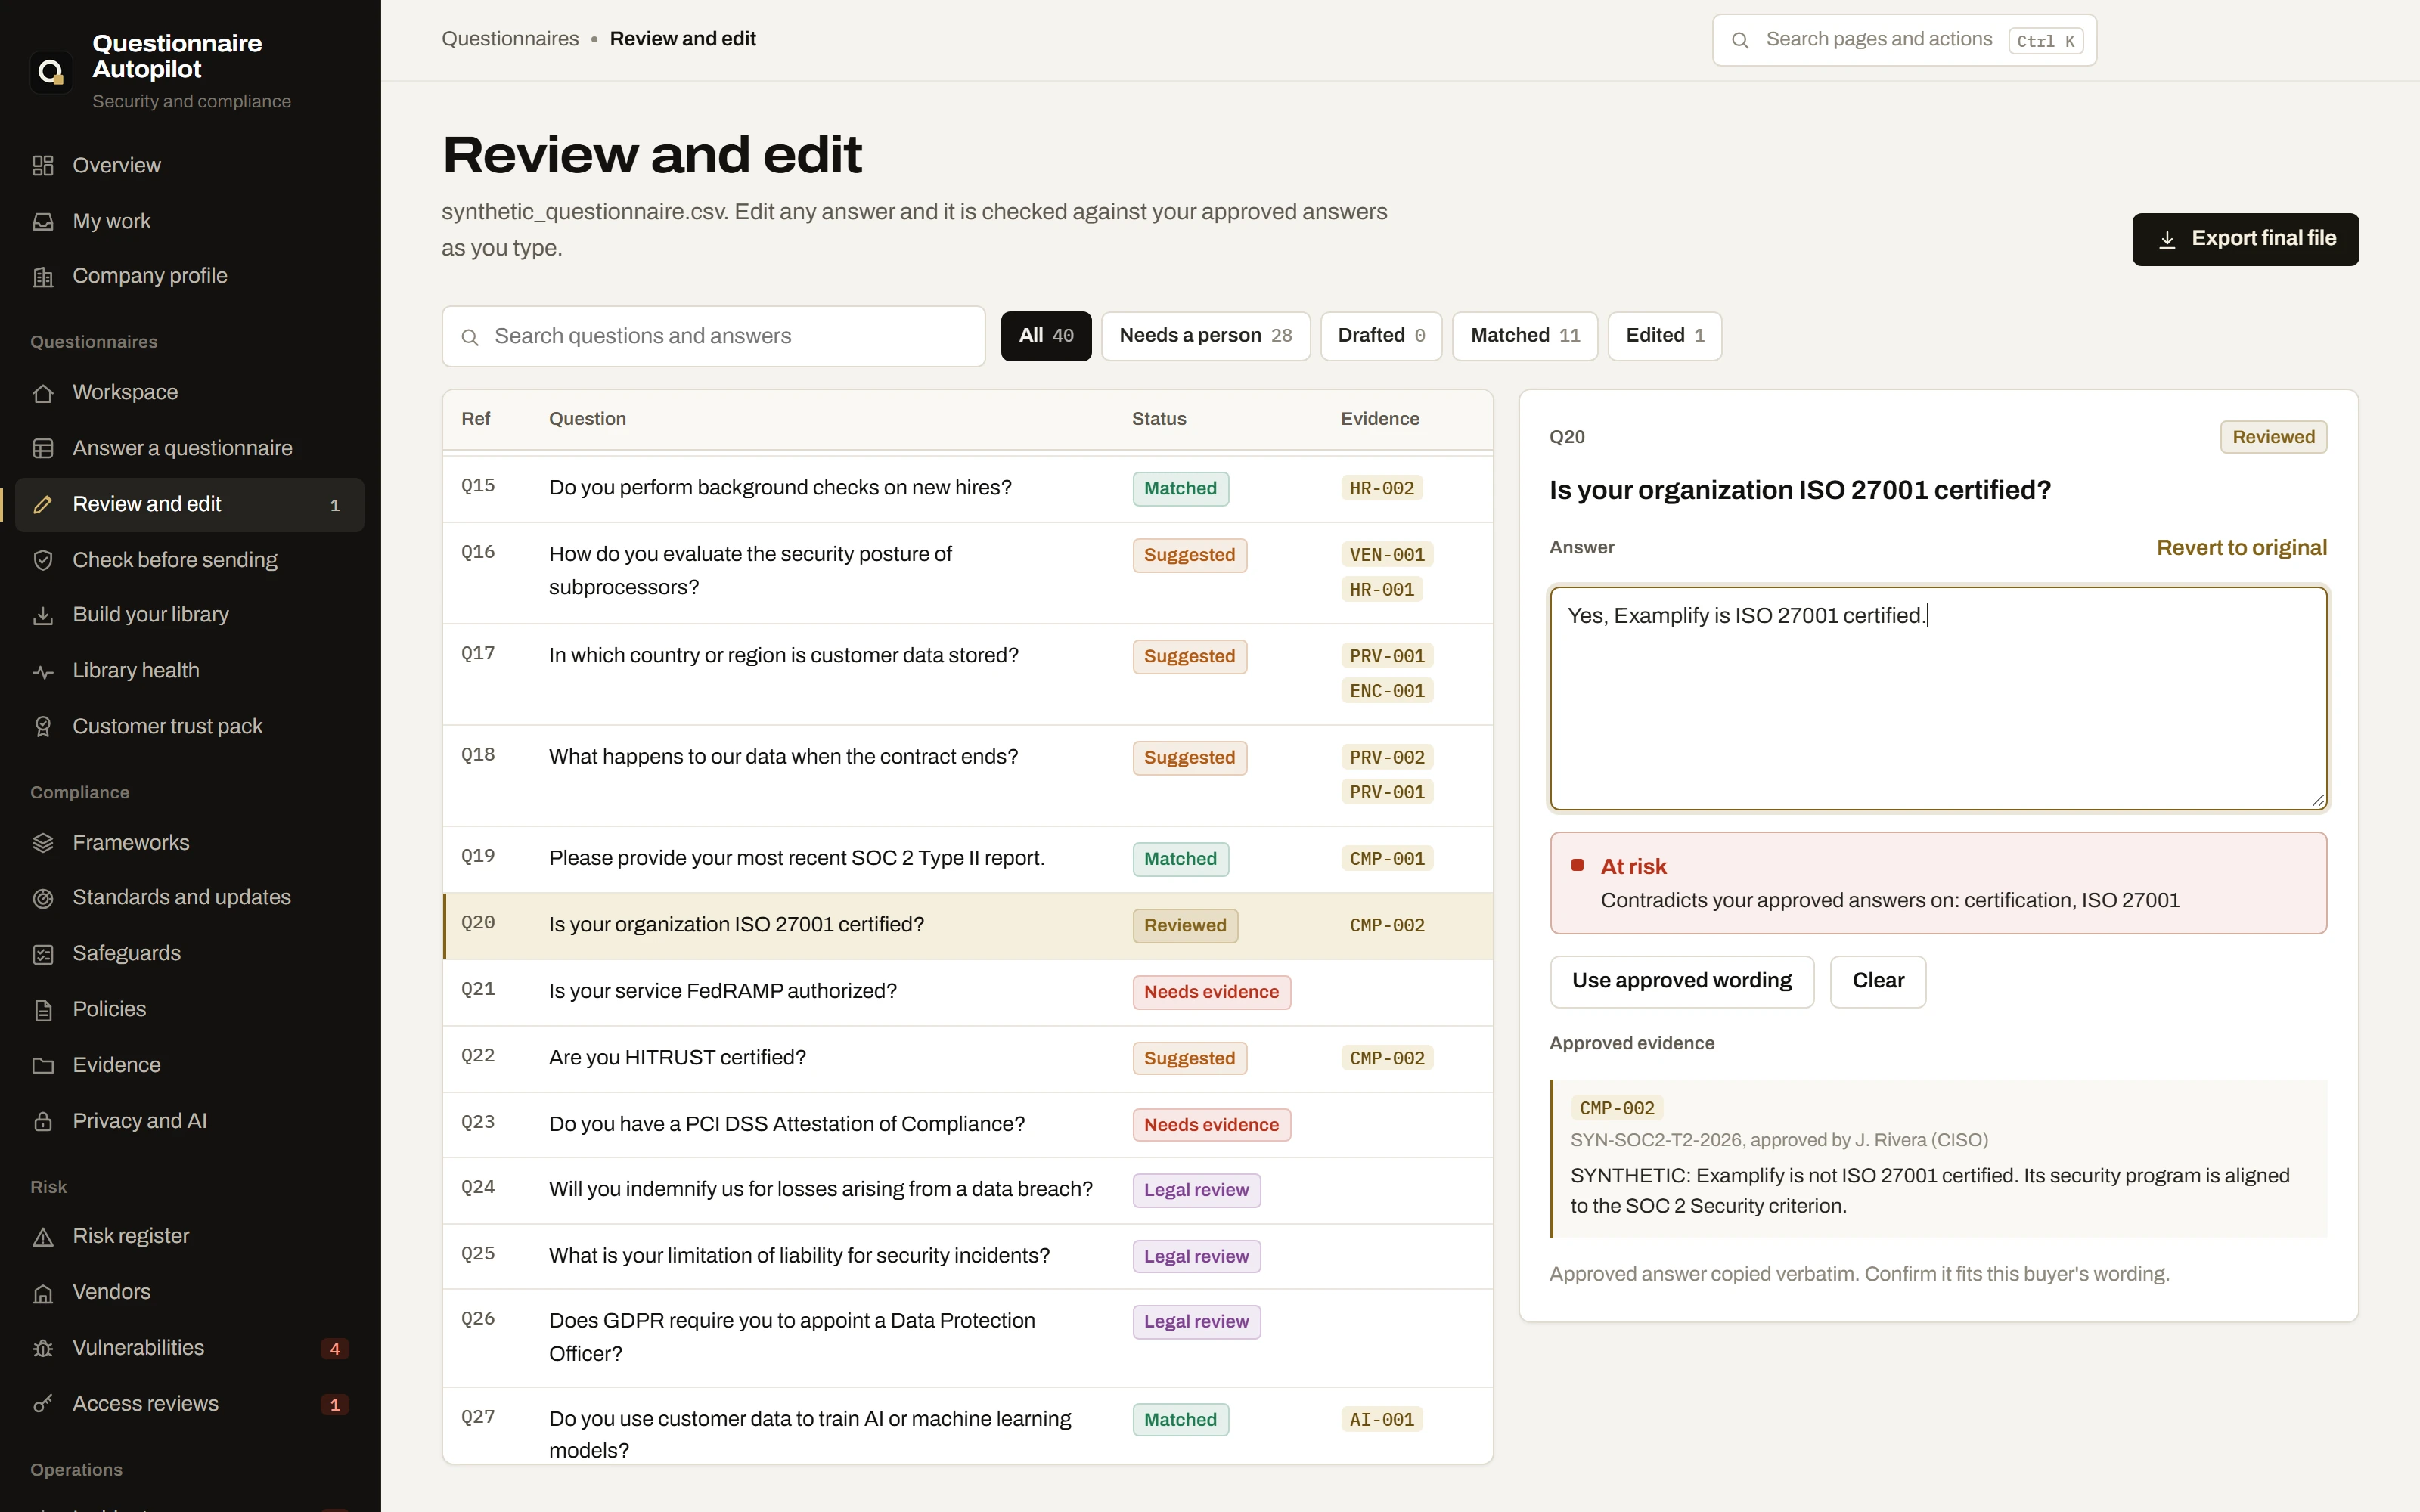
Fill the buyer's own spreadsheet from answers your team approved. Questions without evidence, legal questions and suspicious cells are set aside for a person. The claim guard checks every edit and the final file before it is sent, so nothing claims more than you can prove.

  • Optional AI drafting with a model on your computer or your own cloud key
  • A customer trust pack from the statements you marked shareable
The questionnaire workflow
Review and edit: an answer beside its approved evidence, with an unsupported claim marked At risk
06 Evidence and automated checks

Evidence ready before the auditor asks.

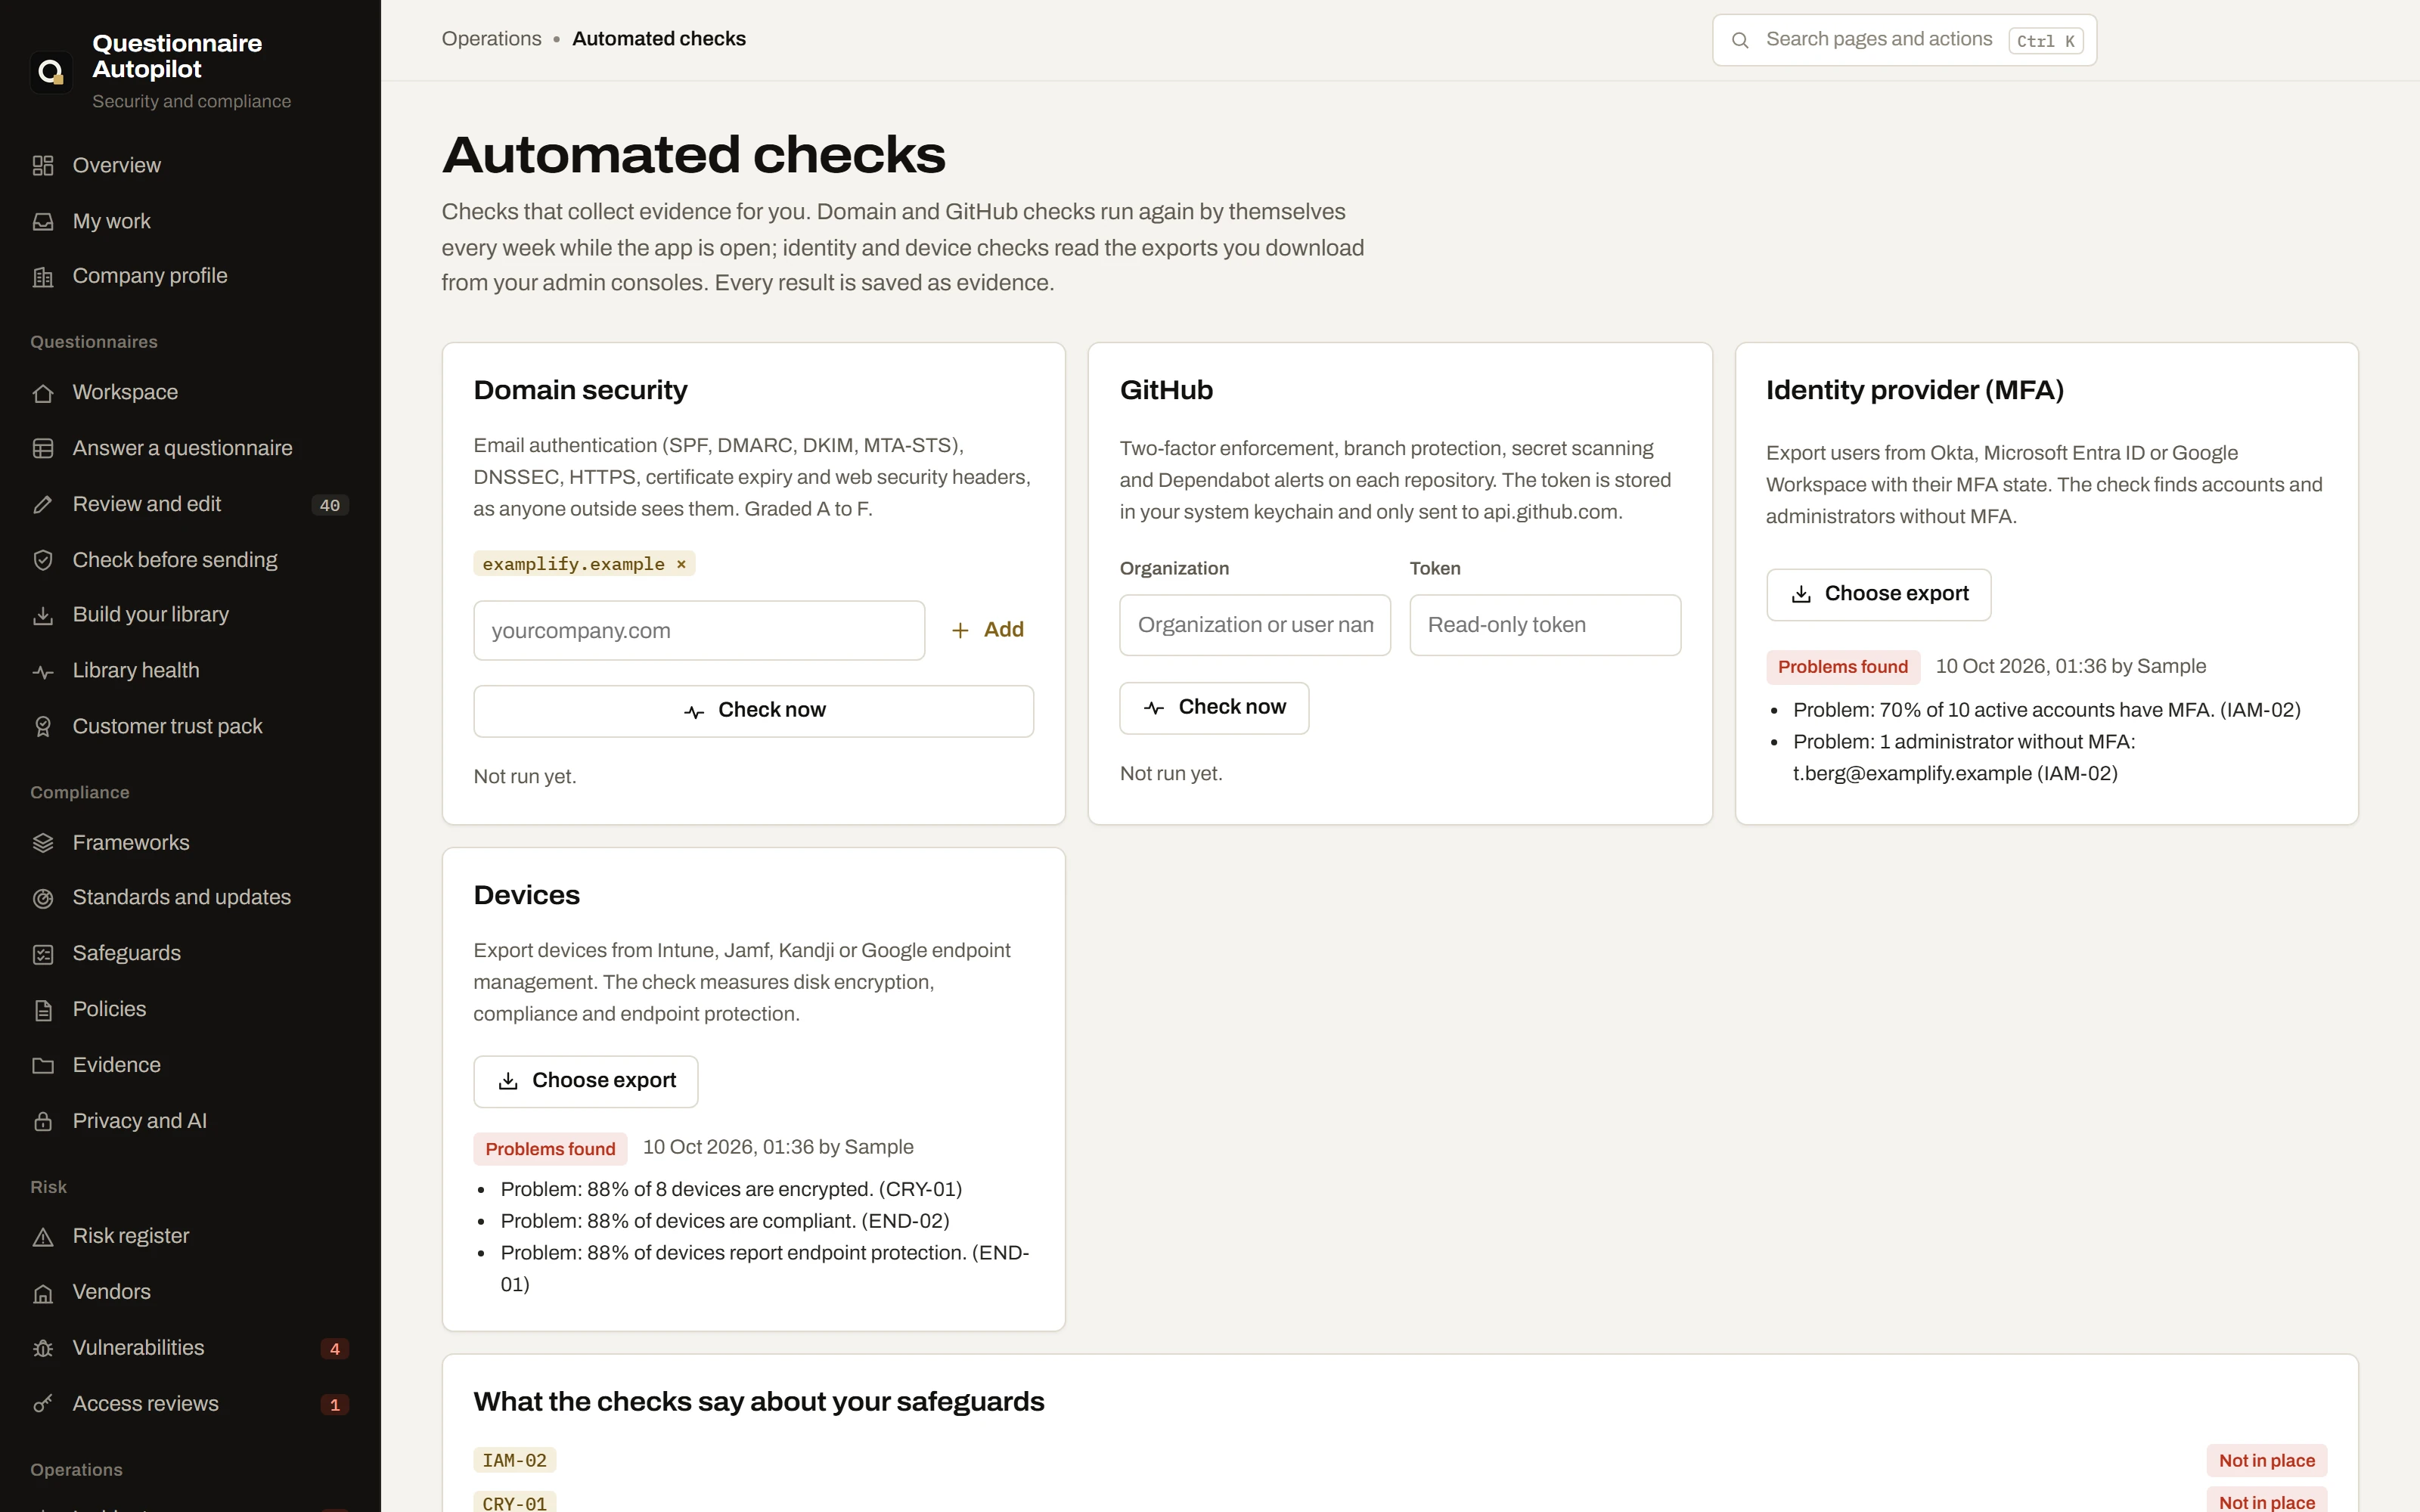
Attach screenshots, exports and reports to each safeguard; each file is stored with its SHA-256 checksum and an expiry date if it has one. Checks run every week and file their own results: your domains' email and web security, your GitHub settings, and the MFA and device exports from your identity provider and device management.

  • Domain grades A to F: SPF, DKIM, DMARC, MTA-STS, DNSSEC, certificates, TLS and security headers
  • One audit package zip with every document and evidence file, and an index of checksums
Evidence in the guide
Automated checks for domain security, GitHub, the identity provider and devices, with what they mean for each safeguard
07 Vulnerabilities and access

Every finding has a date. Every account has an owner.

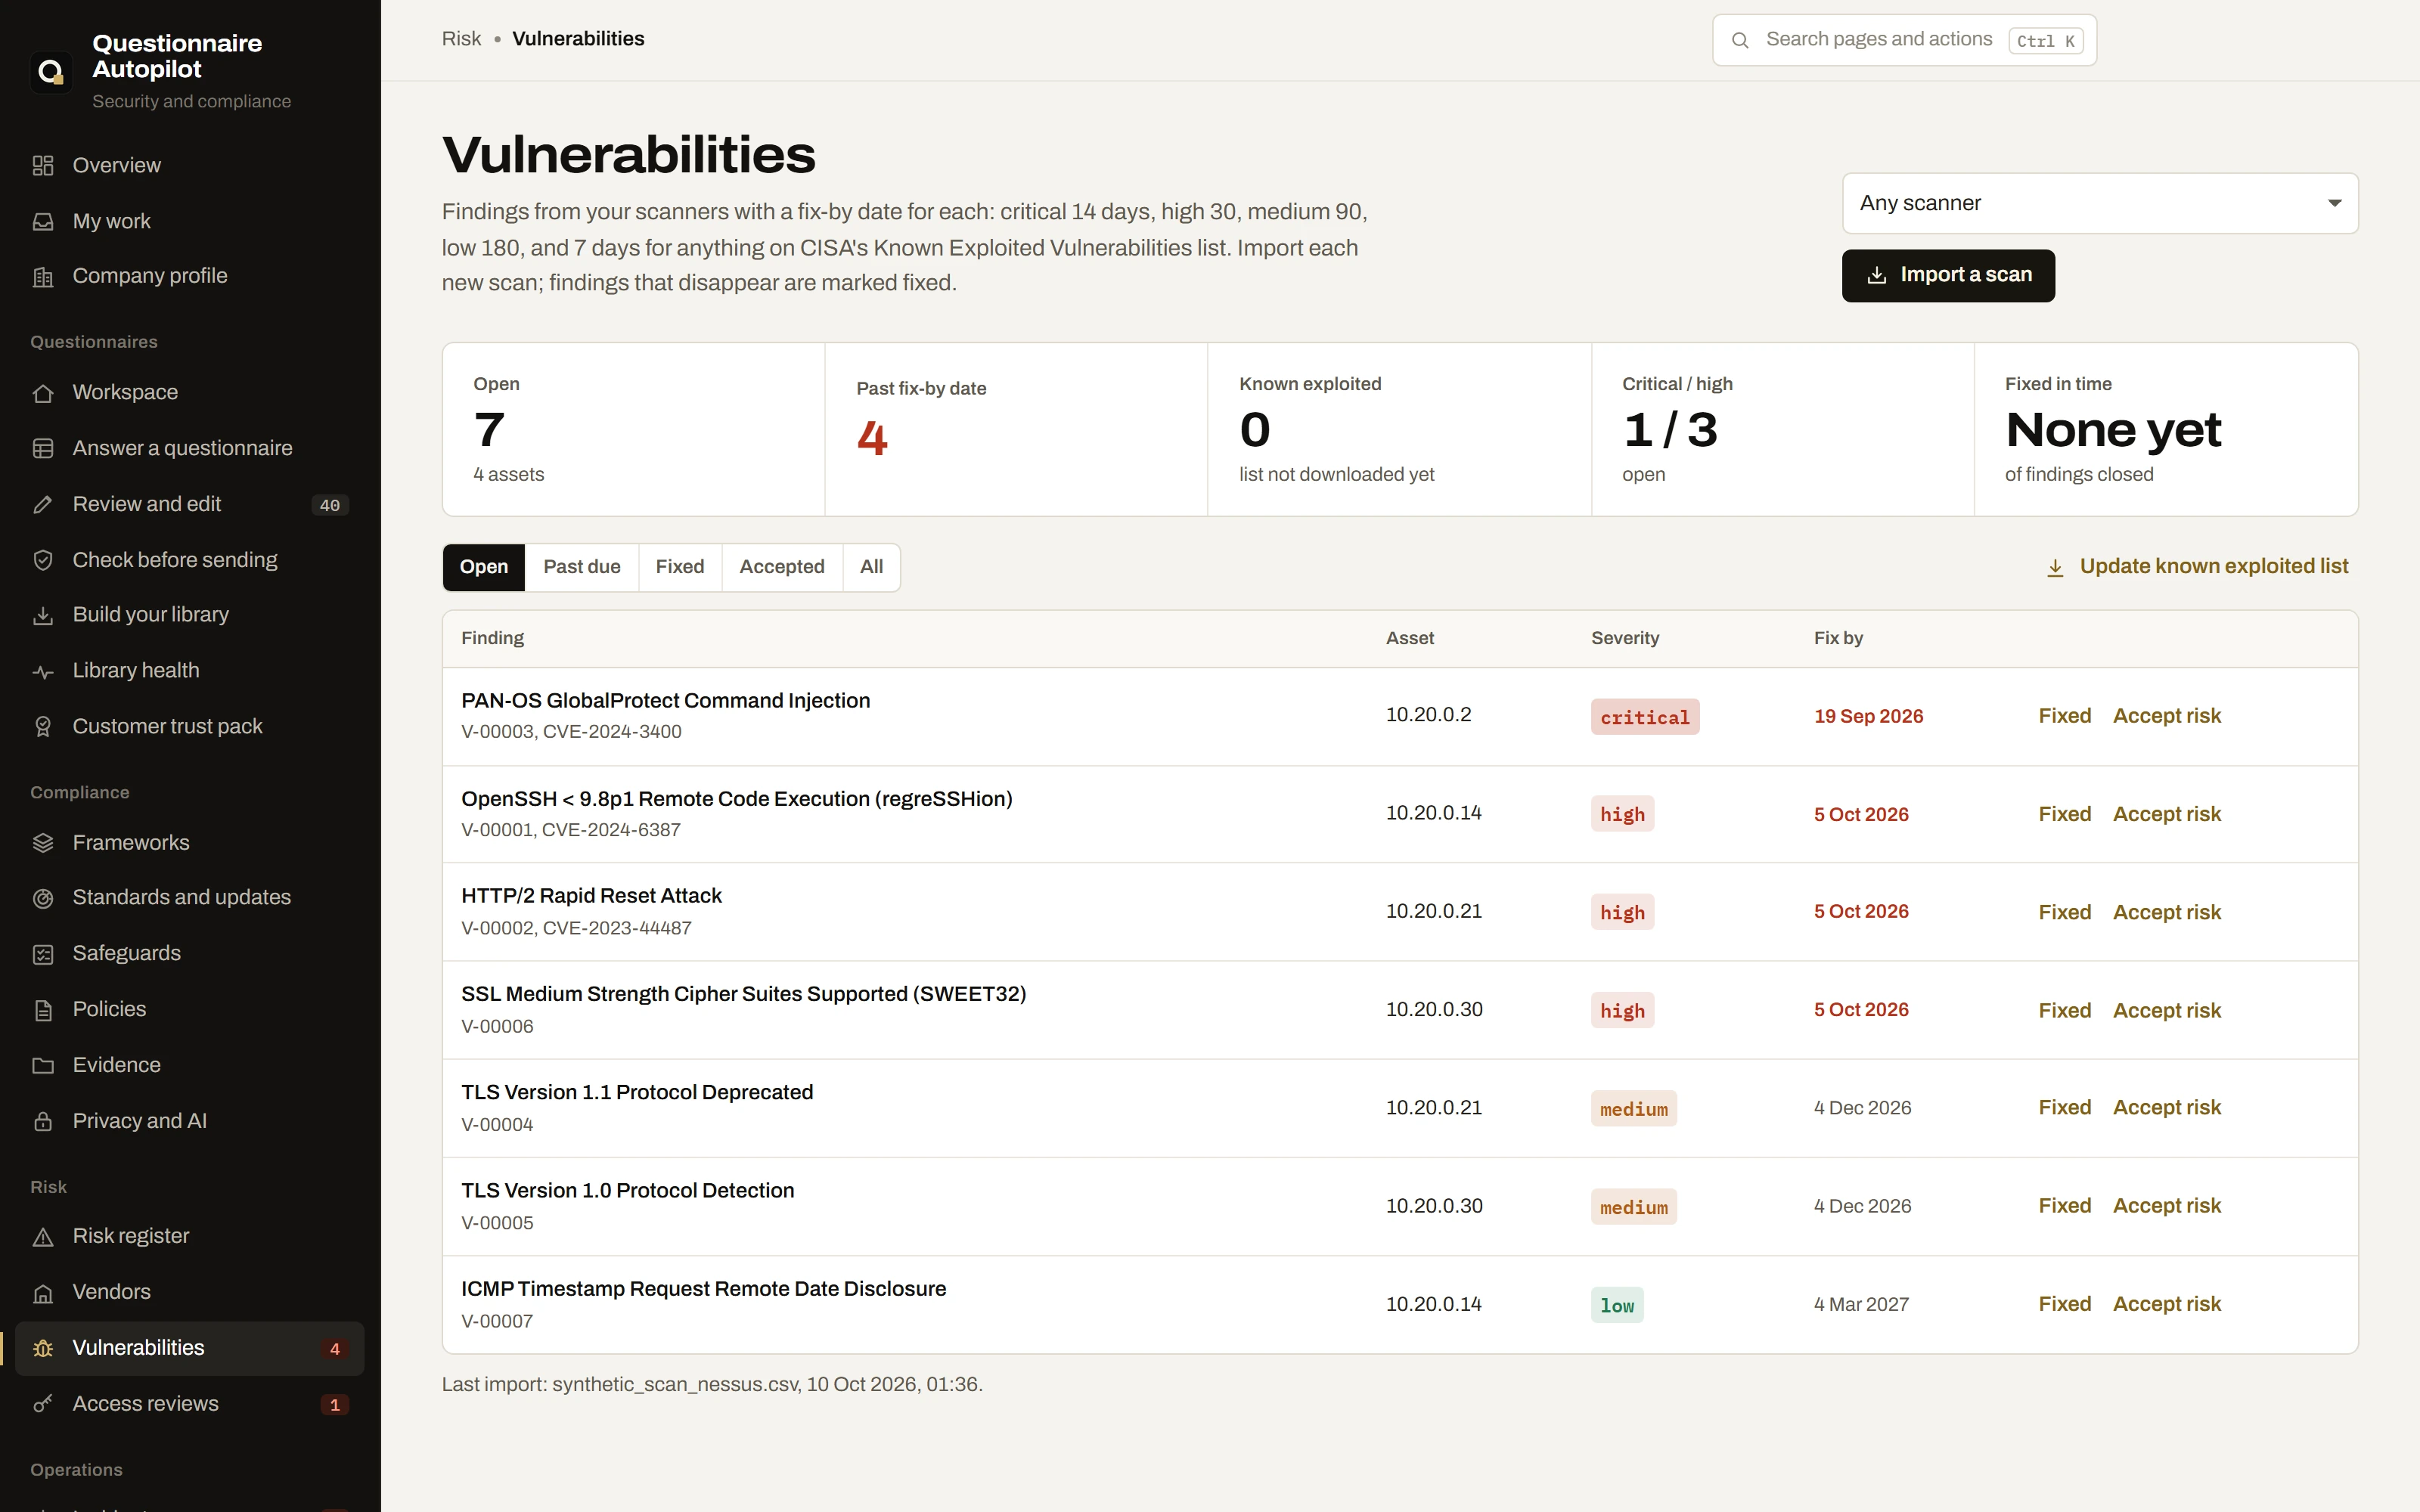
Import scans from Nessus, Qualys, Microsoft Defender or OpenVAS. Each finding gets a fix-by date from its severity, with 7 days for anything on CISA's Known Exploited Vulnerabilities list, and findings that disappear from the next scan are closed. Review who has access to each system from its user export: administrators, accounts without MFA, unused accounts and people who left are flagged for a decision.

  • Accepted risks need a written reason, kept for the auditor
  • The signed-off access review is saved as evidence
Vulnerabilities in the guide
Scanner findings with severity, asset and fix-by dates, four of them past due
08 Privacy, AI and your team

Records of processing, an AI inventory, a shared program.

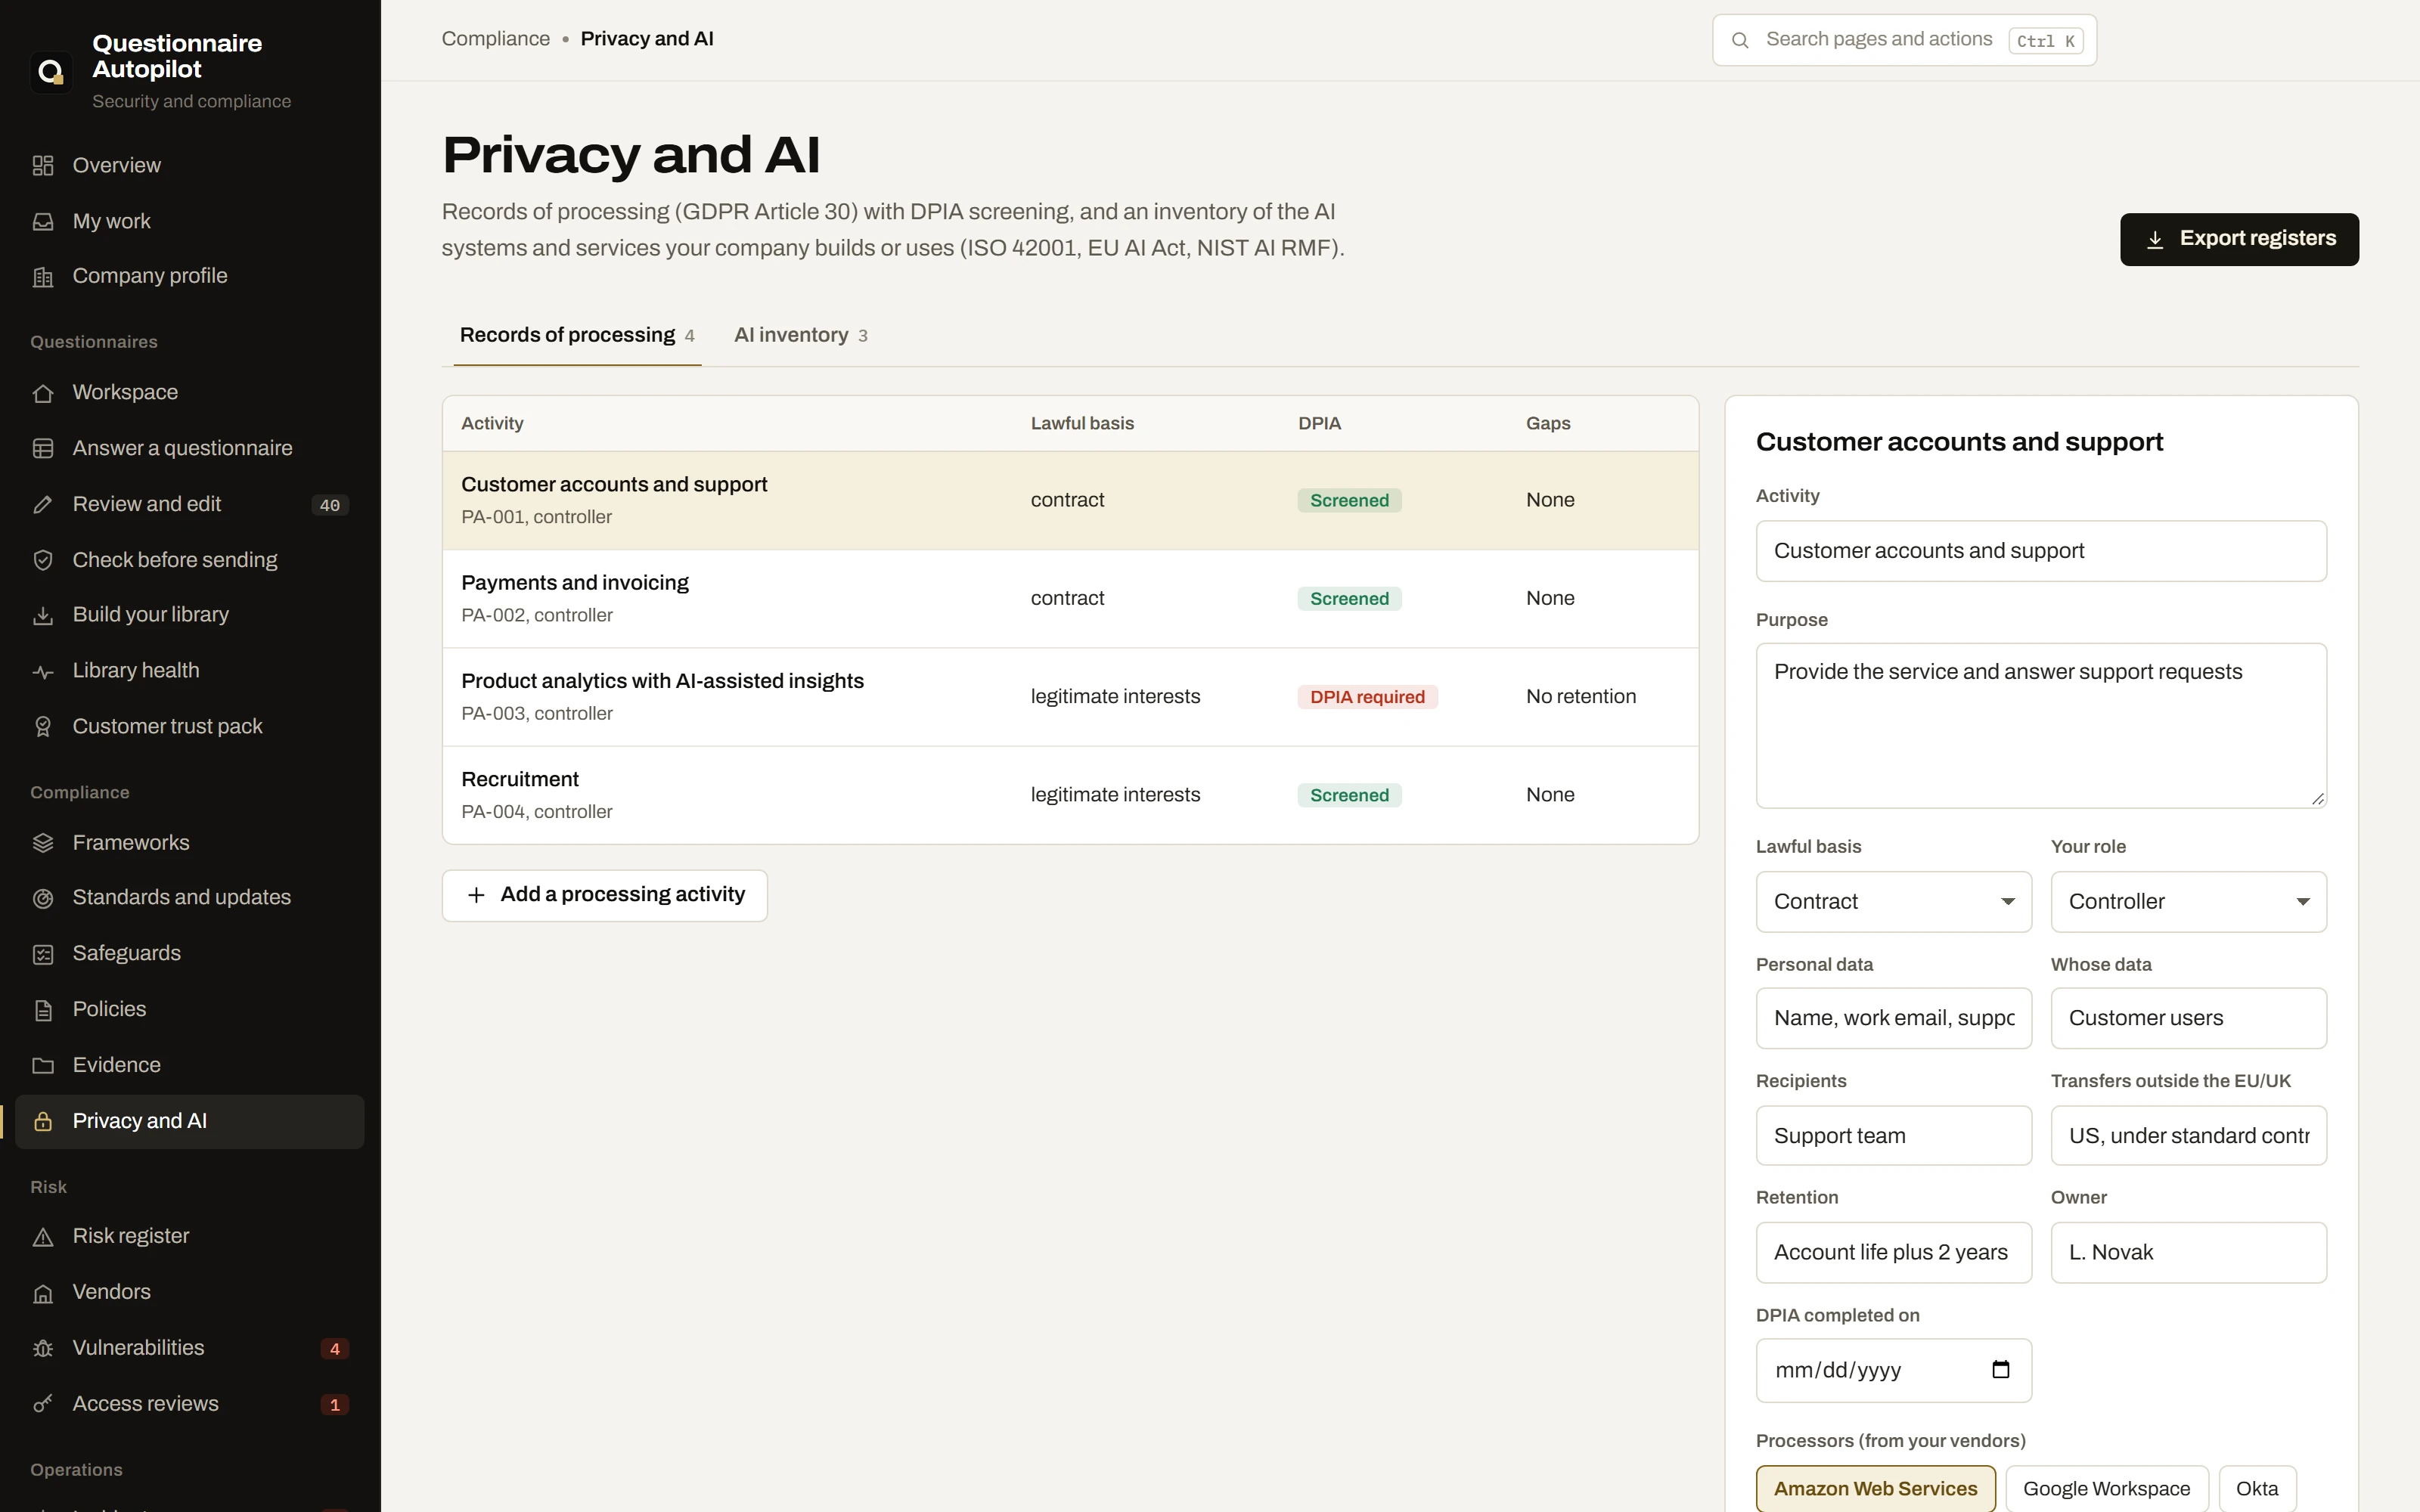
Keep records of processing with DPIA screening and an inventory of the AI tools your company uses or builds. Put the program in a folder your team shares and everyone works on the same one, with locked saves and an activity log that names who changed what.

  • A trust center website with your safeguards, subprocessors, policies and security.txt, to host anywhere
  • My work: each person sees the safeguards, risks, reviews and findings assigned to them
Privacy and AI in the guide
Records of processing with lawful basis, DPIA screening and gaps

The rest of the job, included.

Small details that save hours when the auditor, the insurer or the customer asks.

Calendar

Compliance calendar

Access reviews, restore tests, training, penetration tests, vendor and policy reviews, each with its next due date.

Reports

Leadership report

Posture score, readiness, heat map, top risks, vendors, incidents and next steps, in one document.

Assistant

Intellinaire

Ask about your gaps, a safeguard, an incident or a customer notice. It reads your program and proposes changes you approve.

Library

Answer library health

Expired, expiring and contradictory approvals found before they put a wrong answer in front of a buyer.

Trust

Customer trust pack

A security overview page built only from statements you marked shareable, for sales and procurement.

Automation

Command line

Readiness, reports, scan imports, audit packages and the weekly checks from scripts and scheduled jobs: qa program run-checks.

Vendors

Vendor domain grades

See any vendor's email and web security from the outside, and list the ones that process customer data as subprocessors.

Audit trail

Activity log

Every change to the program with the time and the person's name, included in the audit package.

People

Training and sign-off

Security awareness, phishing and secure coding records, and which policy version each person signed.

Standards

Standards watch

The edition each framework follows and every dated change: in force, coming, proposed or paused. The EU AI Act delay, CMMC Phase 2 and the HIPAA proposal are already in it.

Updates

Signed standards updates

When a standard changes, install the update from inside the app. See every added, removed and renumbered requirement and your readiness before and after, then approve.

Contracts

Your own frameworks

Import a customer's security exhibit or an internal standard from a spreadsheet. Each requirement is mapped to your safeguards for you to confirm, and gets readiness like SOC 2.

History

Readiness history

Posture and readiness recorded every day you work, with named records before an audit or a standards update, so progress is easy to show.

Safety

Daily backups

A copy of the program every day and before every large change, the last 30 kept. Restore any of them in two clicks.
Private by design

Your security program never leaves your computer.

A security program describes exactly where a company is weak. It should not live on someone else's server. Questionnaire Autopilot is desktop software: it has no account, keeps no copy of your data and works offline.

Runs on your computerThe app listens only on this computer, with a one-time secret per session.
Nothing uploadedUnless you choose a cloud AI service or web search. Automated checks only look up the domains and GitHub account you add.
Files you ownWord, Excel, CSV and HTML. Nothing locked in a format.
License check onlyActivation sends the key and a computer label. Nothing else.

Check the fit before you buy.

Hosted platforms connect live to dozens of cloud services and host the auditor relationship for you. If you need that, they are worth their price. If you want the complete program, private and paid for once, this is it.

Questionnaire AutopilotHosted compliance platforms
Price$99 onceAnnual subscription, often several thousand dollars a year
Where your data livesOn your computerOn the vendor's servers
Framework readiness, policies, risks, vendors, incidentsIncludedIncluded
Security questionnaires from approved evidenceIncludedOften an add-on
Evidence files, audit package and activity logIncludedIncluded
Vulnerability tracking with fix-by datesIncluded, from scanner exportsOften an add-on
Access reviews, staff training and policy sign-offIncludedIncluded
Privacy and AI governance (GDPR, ISO 42001, EU AI Act)IncludedOften an add-on
Automated evidence collectionDomains, GitHub, identity and device exports, weeklyLive connections to many cloud services
Trust centerA website you host anywhereHosted for you
Team useShared folder with locking and an activity logLive multi-user web app
When a standard changesDated watch list and signed updates you preview and approveThe vendor updates the platform
Your own frameworks and customer contract requirementsIncluded, imported from a spreadsheet and mapped for youOften a higher tier
Backups of your programDaily, restore any of the last 30Managed by the vendor
Auditor marketplaceNo: bring your own auditorOften

The app helps you prepare. It does not certify your company or replace an auditor; readiness shows your own assessment.

License and download

$99 USD.
One payment.

One organization, for internal use on up to three computers it owns or controls. Updates within the version are included. Optional cloud AI services have their own charges.

What is included, requirements and refunds

Questionnaire Autopilot

$99USD, once

  • Security program: 16 frameworks, safeguards, evidence, policies, risks, vendors, vulnerabilities, access reviews, incidents, calendar, reports
  • Questionnaires, review, pre-send check, library and trust pack
  • Intellinaire assistant with your chosen model
  • Windows, macOS and Linux
Platform

Windows 10 and 11, 64-bitQuestionnaireAutopilot-1.7.4-Windows-x64.zip

Buy for WindowsTry it free for 14 days

Secure checkout, tax, and delivery are handled by Lemon Squeezy, our merchant of record. Read our 14-day refund policy.

Free email security checkSPF, DMARC, DKIM and MTA-STS for any domain, graded A to F.User guideInstall, every module step by step, with HD videos of each task.ArticlesQuestionnaire formats, final checks and a free library template.SupportQuestions about installing, licensing or using the app.